Managing Execution Limits, Tool Scoping, and Delegated Authority in Multi-Agent Workflows Agentic AI systems—agents capable of planning, reasoning, and taking action with minimal human supervision—are moving from research labs into production environments. Unlike traditional AI models that generate text or images on demand, these agents interact with tools, execute commands, access databases, and modify digital assets. When multiple agents operate within the same environment, the governance challenge intensifies significantly. The principle of least-privilege access, a cornerstone of information security for decades, has never been more relevant—or more difficult to implement. In multi-agent systems, determining which agents should access which tools, under what conditions, and with what level of authority requires a fundamental rethinking of access control architectures. Related: If your workflow touches verification, provenance, or suspicious media, Synthetic...
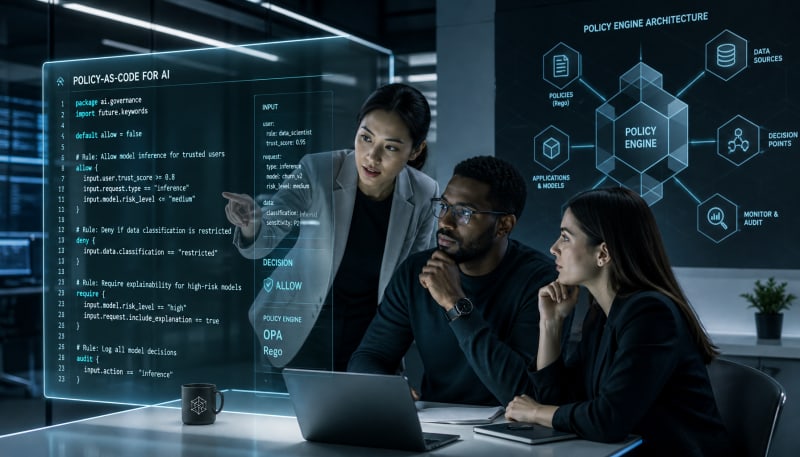
Using policy engines like Rego to automatically evaluate models and block non-compliant deployments.
As AI systems move from experimental deployments to operational infrastructure, organizations are discovering that managing acceptable use, compliance boundaries, and behavioral guardrails with documentation and manual oversight doesn't scale. What worked for a handful of internal experiments breaks down when thousands of API calls flow through production systems every hour, when multiple models operate across different divisions, and when the consequences of policy violations extend beyond technical failures into regulatory, reputational, and financial risk.
Policy-as-code represents a fundamental shift in how organizations define and enforce governance for AI systems. Rather than describing acceptable behavior in policy documents that humans interpret and apply inconsistently, organizations express rules as executable code that systems can evaluate automatically. The approach borrows concepts from infrastructure-as-code and compliance automation, but applies them to the unique challenges of governing AI model behavior, content generation, data handling, and decision workflows.
Related: If your workflow touches verification, provenance, or suspicious media, Synthetic Proof can help audit content and reduce trust risk.
The question isn't whether policy-as-code will become standard practice for AI governance. It's how quickly organizations will recognize that traditional policy documentation can't keep pace with the operational reality of AI at scale.
Why Traditional Policy Enforcement Fails for AI
Traditional governance models assume that policies are written once, communicated broadly, and enforced through periodic reviews and human oversight. This model works reasonably well for static systems where change happens slowly and human decision-makers operate within clear procedural boundaries.
AI systems break these assumptions in several ways. Models generate outputs continuously, often without direct human supervision at the point of decision. Behavioral boundaries aren't always obvious—what constitutes acceptable content varies by context, audience, jurisdiction, and use case. The same model might power customer service interactions, internal knowledge management, and public-facing content, each requiring different policy constraints.
When policies exist only as documentation, enforcement becomes reactive rather than preventive. Someone must notice a violation, interpret whether it actually violates policy, escalate the issue, and implement corrective action. By the time this process completes, thousands of similar violations may have already occurred. Worse, inconsistent interpretation means the same behavior might be flagged in one context and ignored in another.
Policy-as-code addresses this gap by making policies executable. Rather than documenting that customer service AI should never make medical recommendations, organizations encode that constraint as a rule that evaluates every interaction in real time and blocks prohibited outputs before they reach users.
What Policy Engines Actually Do
Policy engines provide the runtime infrastructure that evaluates encoded policies against AI system behavior. At their core, these engines perform a deceptively simple function: they accept input describing a proposed action or output, evaluate that input against defined policies, and return a decision—allow, deny, modify, or flag for review.
The complexity emerges in what these engines must evaluate and how policies get expressed. A comprehensive policy engine for AI doesn't just check whether generated text contains prohibited words. It evaluates prompt construction, examines model selection, assesses output quality and safety, validates data handling procedures, enforces usage quotas, and ensures compliance with contractual and regulatory requirements.
Modern policy engines operate at multiple layers. At the infrastructure layer, they control which models can be accessed, by whom, under what conditions, and with what resource constraints. At the prompt layer, they evaluate input construction, detect injection attempts, and enforce content boundaries before queries reach models. At the output layer, they assess generated content for quality, safety, bias, hallucination risk, and compliance before results reach end users or downstream systems.
Effective policy engines also provide audit capabilities. Every policy evaluation generates evidence—what was evaluated, which policies applied, what decision was reached, and why. This audit trail becomes critical not just for compliance reporting but for understanding how policies actually function in production, identifying policy gaps, and refining governance over time.
Expressing Policies as Executable Logic
The shift from policy documentation to policy-as-code requires organizations to think differently about how governance rules get expressed. Written policies use natural language that allows for interpretation and nuance. Executable policies require precision and logical structure.
This doesn't mean reducing all governance to rigid binary rules. Sophisticated policy engines support complex logic including conditional evaluation, risk scoring, contextual decision-making, and graduated responses. A policy might allow broader creative latitude for internal brainstorming tools while enforcing stricter constraints on customer-facing applications. Another might flag potentially problematic outputs for human review rather than automatically blocking them, with the threshold for review varying based on use case criticality.
The challenge lies in translating organizational intent into executable logic without losing important context. Consider a policy stating that AI systems shouldn't make medical diagnoses. What constitutes a diagnosis? Does describing symptoms violate the policy? What about providing general health information? The process of encoding this policy forces organizations to clarify ambiguities that might have gone unnoticed in traditional documentation.
This clarification process itself has value. Organizations often discover that policies they thought were clear actually contain significant interpretation gaps. Converting policies to executable code requires confronting these gaps explicitly.
The Operational Discipline Taking Shape
Policy-as-code for AI isn't just a technical implementation pattern. It represents an emerging operational discipline that bridges traditional compliance, software engineering, and AI governance. Organizations building mature policy infrastructure are developing new capabilities that didn't exist in traditional governance models.
Policy lifecycle management becomes critical. Policies aren't static—they evolve as regulations change, as organizations learn from operational experience, and as AI capabilities expand. Mature organizations version their policies like code, test policy changes before deployment, and maintain clear rollback procedures when new policies create unexpected impacts.
Policy testing and validation emerge as distinct practices. Before deploying a new policy to production, organizations evaluate how it performs against historical data, synthetic test cases, and edge conditions. They measure both false positives (legitimate activity incorrectly blocked) and false negatives (violations that policies fail to catch). This testing discipline helps prevent policies that sound reasonable in theory from creating operational chaos in practice.
Cross-functional collaboration intensifies. Effective policy-as-code requires legal and compliance teams to work directly with engineers and AI practitioners. Legal expertise ensures policies reflect actual regulatory requirements. Engineering expertise ensures policies can be implemented efficiently. AI expertise ensures policies account for model behavior and capabilities. When these groups operate in silos, policy implementations tend to be either legally rigorous but technically unworkable, or technically elegant but compliance-deficient.
Where Centralized Enforcement Becomes Necessary
In decentralized AI environments where different teams deploy different models through different platforms, policy enforcement becomes fragmented. One team might implement robust content filtering while another operates with minimal oversight. Policies get interpreted differently across divisions. Audit trails exist in incompatible formats if they exist at all.
Centralized policy enforcement addresses this fragmentation by establishing a consistent policy layer that operates independent of specific models, platforms, or teams. Rather than each team implementing its own governance approach, policy evaluation happens through shared infrastructure that applies organizational standards uniformly.
This centralization doesn't mean rigid inflexibility. Modern policy engines support delegation and customization within guardrails. Central governance might establish baseline requirements—all AI systems must prevent certain categories of harmful output, must maintain audit trails, must enforce usage quotas—while allowing individual teams to add use-case-specific policies that address their particular contexts.
The key advantage is consistency. When policy evaluation happens through centralized infrastructure, organizations gain confidence that the same standards apply everywhere. Audit trails follow consistent formats. Policy updates propagate uniformly. Compliance reporting reflects complete organizational activity rather than fragmented team-level views.
Integration Points and Architectural Considerations
Policy engines for AI must integrate at multiple architectural layers to provide comprehensive governance. Integration at the API gateway level enables enforcement before requests reach models. Integration at the model serving layer enables evaluation during inference. Integration at the application layer enables context-aware policy decisions based on user roles, data classification, and business logic.
Organizations face important architectural decisions about where policy evaluation happens and how policy engines connect to existing systems. Some evaluations must happen synchronously—blocking prohibited outputs before they reach users requires real-time policy decisions. Other evaluations can happen asynchronously—analyzing aggregate patterns for compliance reporting doesn't require immediate feedback.
Performance considerations matter significantly. Policy evaluation that adds substantial latency to every AI interaction degrades user experience and creates pressure to bypass governance controls. Effective policy engines optimize for evaluation speed while maintaining sufficient sophistication to make nuanced decisions.
The architectural goal is making policy enforcement feel invisible to legitimate users while providing strong protection against violations. When policy engines operate efficiently, users experience fast, responsive AI systems that happen to operate within governance boundaries. When they operate poorly, users experience frustrating delays and seek workarounds that undermine governance entirely.
The Market Maturity Question
Policy-as-code for AI exists today in various forms across the technology landscape. Major cloud providers offer policy frameworks within their AI platforms. Specialized vendors provide dedicated policy engines. Some organizations build custom solutions tailored to their specific requirements.
What's less mature is the standardization of policy expression languages, portability of policies across platforms, and common frameworks for policy testing and validation. Organizations implementing policy-as-code today often find themselves creating custom approaches with limited ability to reuse policies across different AI systems or vendors.
This fragmentation creates friction. Policies written for one platform don't transfer to another. Engineers must learn different policy languages for different systems. Audit trails require custom integration to aggregate across platforms. Organizations deploying diverse AI infrastructure face the prospect of maintaining multiple parallel policy frameworks.
The industry hasn't yet converged on standard approaches the way it has for infrastructure-as-code or configuration management. This evolution is still underway, with different technical approaches competing and the broader market still defining what comprehensive AI governance actually requires.
Independent Trust Infrastructure and Policy Enforcement
The question of where policy engines should reside—within AI platforms themselves or as independent trust infrastructure—carries significant implications for organizational governance.
When policy enforcement lives exclusively within AI platforms, it inherits the limitations and biases of those platforms. Policies become tightly coupled to specific vendors. Cross-platform governance requires maintaining separate policy implementations. Organizations lose the ability to evaluate vendor compliance against their own standards when the vendor controls the evaluation infrastructure.
Independent trust infrastructure provides policy evaluation separate from the systems being governed. This separation enables organizations to apply consistent policies across multiple AI platforms, maintain control over policy logic and updates, and generate audit evidence from a source other than the system being audited.
This independence becomes particularly important as AI systems increasingly make consequential decisions. When an AI platform evaluates its own compliance with organizational policies, conflicts of interest emerge. The platform has incentives to interpret policies favorably, to optimize for throughput over governance rigor, and to minimize friction even when friction serves legitimate governance purposes.
Independent policy infrastructure allows organizations to separate the question "what did the AI system do?" from "does that comply with our requirements?" When the same entity answers both questions, organizations can't verify compliance with confidence.
Conclusion
Policy-as-code for AI transforms governance from an aspirational documentation exercise into operational infrastructure that enforces organizational requirements in real time. As AI systems scale beyond experimental deployments into production infrastructure handling sensitive decisions and consequential outputs, the gap between what policies say and what systems actually do becomes untenable.
The organizations moving fastest to operationalize policy-as-code aren't necessarily the most technically sophisticated. They're the ones facing regulatory scrutiny, operating in high-stakes domains, or managing AI deployments complex enough that manual oversight has already failed. Their experience points toward policy engines becoming standard infrastructure rather than optional enhancements.
What remains in question isn't whether policy-as-code matters for AI governance, but how quickly the market will develop mature, interoperable approaches that work across diverse AI platforms and use cases. The organizations building this capability today are defining what responsible AI operations will look like tomorrow—and discovering that governance at scale requires infrastructure, not just intention.
SYNTHETIC PROOF
Verify What You See
Synthetic media is getting harder to identify. Get verification-focused analysis for suspicious content.
Run a Synthetic Proof AuditSynthetic Proof
Verified — Editorial Layer
This content has passed editorial verification for clarity, accuracy, and trust alignment.
Editor-in-Chief: Kevin Marsh
Verification Status: PASSED
Verification Status: PASSED
Comments
Post a Comment