Managing Execution Limits, Tool Scoping, and Delegated Authority in Multi-Agent Workflows Agentic AI systems—agents capable of planning, reasoning, and taking action with minimal human supervision—are moving from research labs into production environments. Unlike traditional AI models that generate text or images on demand, these agents interact with tools, execute commands, access databases, and modify digital assets. When multiple agents operate within the same environment, the governance challenge intensifies significantly. The principle of least-privilege access, a cornerstone of information security for decades, has never been more relevant—or more difficult to implement. In multi-agent systems, determining which agents should access which tools, under what conditions, and with what level of authority requires a fundamental rethinking of access control architectures. Related: If your workflow touches verification, provenance, or suspicious media, Synthetic...
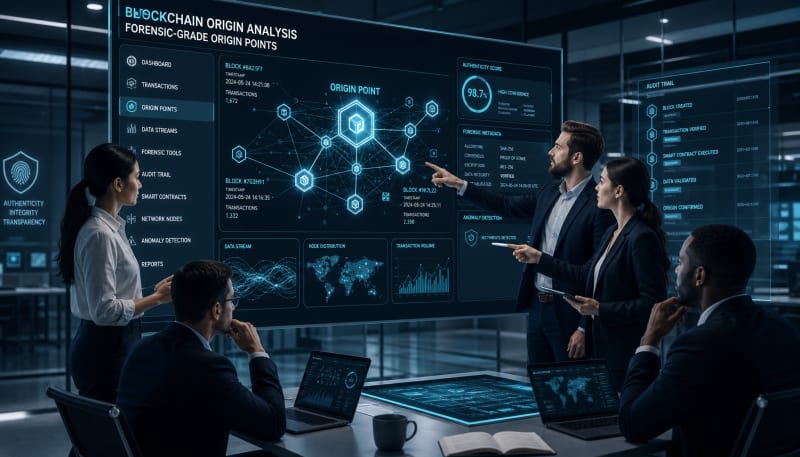
How NextGen content pipelines are replacing unverified uploads with ironclad, physical-world proof.
A photograph submitted as evidence in litigation now carries the same verification burden as a document that could have been edited in hundreds of places by dozens of tools. A product demonstration video arrives without any record of how it was created, altered, or assembled. A compliance audit requires proof of AI system behavior, but the only available documentation is a PDF someone exported yesterday.
The ability to falsify digital artifacts has outpaced the ability to verify them. Not incrementally—structurally. The tools that create, edit, and manipulate content have become so sophisticated and accessible that traditional methods of establishing authenticity no longer function reliably. Metadata can be stripped. Timestamps can be altered. File histories can be reconstructed.
The value of provenance ultimately depends on whether organizations can turn evidence into confident decisions. Synthetic Proof helps examine that broader trust picture across AI content and workflows.
What's emerging in response isn't just better verification—it's a fundamental rethinking of where authenticity begins. Organizations building for regulatory scrutiny, legal defensibility, or operational accountability are moving toward something more rigorous: forensic-grade origin points captured at the moment of creation, before any opportunity for modification exists.
Verification Worked When Manipulation Was Hard
For decades, digital verification relied on signals embedded after creation. A timestamp on a file. Metadata indicating the camera model. EXIF data showing GPS coordinates. These signals worked because manipulation required specialized knowledge, expensive software, and detectable traces.
That assumption no longer holds. Generative AI tools can produce photorealistic images indistinguishable from photographs. Video editing happens in real-time through browser interfaces. Audio can be cloned from seconds of source material. Even more problematic: these capabilities leave fewer forensic traces than traditional editing once did.
The verification challenge isn't simply that bad actors have better tools. It's that the baseline presumption—that unmanipulated content can be distinguished from manipulated content through post-hoc analysis—has collapsed for many categories of digital artifacts.
When every piece of content could plausibly have been altered, verification becomes a burden rather than a process. Legal teams spend weeks establishing chain of custody for digital evidence. Compliance officers cannot confidently demonstrate that submitted documentation reflects actual system behavior. Communications departments cannot prove marketing assets weren't misleadingly edited.
Post-Creation Verification Inherits Uncertainty
Traditional approaches to digital authenticity operate after the artifact already exists. Something gets created, then someone tries to verify it. This introduces an unavoidable problem: any signal used for verification must itself be verified.
A digital signature proves the file hasn't changed since signing—but not what happened before signing. A blockchain timestamp proves when something was registered—but not whether it was altered before registration. Watermarking proves ownership—but not whether the underlying content is authentic.
Each of these approaches adds a layer of verification to an artifact whose creation history remains opaque. They answer "has this changed since checkpoint X?" but cannot answer "what actually happened during creation?" For workflows requiring forensic-grade assurance, that gap matters.
This is why organizations subject to regulatory scrutiny or legal discovery are increasingly uncomfortable relying solely on post-creation verification. The question isn't whether a timestamp can be trusted—it's whether the artifact being timestamped reflects what it purports to represent.
The Shift Toward Creation-Time Capture
Forensic-grade origin points operate differently. Rather than adding verification after creation, they capture authenticating evidence during creation—before any opportunity for undetected modification.
The principle is straightforward: if you need to prove something wasn't altered, the most defensible approach is capturing its exact state at the moment it came into existence, along with the context explaining how it was created.
This isn't simply logging. It's structured capture of source materials, transformations, tool configurations, timestamp attestations, and environmental context—recorded in a way that makes subsequent tampering either impossible or immediately detectable. The resulting record becomes a creation artifact in its own right, separate from the content it documents.
Organizations implementing this approach are embedding capture mechanisms directly into workflows. When a render completes, the origin record is generated simultaneously. When a document is finalized, its creation lineage is sealed before distribution. When AI generates output, the prompt context and model parameters are captured at inference time.
The result is content that arrives with its own unfalsifiable creation history. Not a claim about authenticity—evidence of it.
What Forensic-Grade Actually Requires
The term "forensic-grade" carries specific implications. It means the captured evidence could withstand expert examination, legal discovery, regulatory audit, or adversarial scrutiny.
That standard requires several technical characteristics working in concert.
First, tamper-evidence that makes any modification to the origin record detectable. This typically involves cryptographic mechanisms that bind the record's components together such that changing any element invalidates the whole. The record must prove its own integrity without requiring trust in the entity that created it.
Second, temporal proof that establishes when the origin point was captured. This goes beyond simply writing a timestamp into a file—it requires anchoring the record to an external, independent time source that cannot be retroactively manipulated.
Third, completeness of lineage. A forensic-grade origin point doesn't just capture the final output—it documents the transformation chain that produced it. What inputs were used. What processes were applied. What parameters governed generation. The record needs to answer "how did this come to exist?" with sufficient specificity that the creation process could be understood or reconstructed.
Finally, independence from the content itself. The origin record must exist as a separate, durable artifact that can be validated even if the original content is modified or destroyed. This allows verification to occur years later, across organizational boundaries, without requiring access to proprietary systems.
Where This Becomes Non-Negotiable
Not every workflow requires forensic-grade origin points. Marketing images, internal presentations, and exploratory prototypes often don't need unfalsifiable provenance.
But certain categories of content are moving toward this standard rapidly.
Legal discovery increasingly involves AI-generated analysis, automated document review, and algorithmically surfaced evidence. Courts are beginning to require documentation of how these systems operated and what outputs they produced. Claims that "the AI said X" require proof—not just testimony.
Financial services firms using AI for credit decisions, fraud detection, or risk assessment face regulatory expectations that they can demonstrate exactly how decisions were reached. Model cards and documentation help, but auditors increasingly want evidence of actual system behavior at decision time, not theoretical descriptions of how systems should behave.
Healthcare organizations deploying diagnostic AI or treatment recommendation systems need to establish that the outputs informing clinical decisions weren't altered post-generation. The consequences of undetected modification—or even the inability to rule it out—create unacceptable liability.
Media organizations authenticating sources, corporations defending against deepfake impersonation, and government agencies establishing chain of custody for digital intelligence all face variations of the same problem: content that matters requires proof of origin that survives scrutiny.
The Workflow Integration Challenge
The technical capability to create forensic-grade origin points already exists. The harder problem is making it practical.
Asking creators to manually document every step of content creation doesn't scale. Requiring specialized tools that disrupt existing workflows creates adoption barriers. Systems that demand human intervention at capture time will be bypassed or forgotten under deadline pressure.
This is why the emerging pattern involves automated capture integrated directly into existing production environments. The origin point gets generated as a natural byproduct of creation, not as an additional step requiring conscious effort.
For rendering pipelines, this means origin capture happens when the render completes—automatically documenting inputs, settings, and outputs without requiring artist intervention. For document workflows, it means capturing lineage at export or publication time, integrated into the same action that produces the final file. For AI systems, it means inference-time logging that generates origin records as outputs are produced.
The design challenge is ensuring that the most trustworthy path is also the path of least resistance. When capturing forensic-grade provenance requires extra work, it becomes optional. When it happens automatically as part of standard workflow, it becomes infrastructure.
Unfalsifiable Doesn't Mean Unexplainable
A common concern with cryptographically secured origin points is that they become black boxes—technically verifiable but humanly incomprehensible.
This represents a design failure, not an inherent limitation.
Forensic-grade origin points should produce two parallel outputs: a cryptographic record that proves integrity and temporal anchoring, and a human-readable manifest that explains what happened. The manifest describes the creation process in plain language. The cryptographic record proves the manifest hasn't been altered.
This separation allows different audiences to interact with the origin point appropriately. Technical auditors can verify cryptographic proofs. Legal teams can review creation manifests without needing to understand hash functions. Regulators can examine workflow documentation knowing it reflects the actual process used.
The goal isn't to make verification require less expertise—it's to ensure that expertise can be applied effectively. An unfalsifiable origin point that nobody can interpret serves no practical purpose.
Final Thoughts
The shift toward forensic-grade origin points represents something more significant than incremental improvement in content verification. It's recognition that digital authenticity cannot be reliably established after the fact when creation and manipulation have become technically indistinguishable.
Organizations facing regulatory scrutiny, legal exposure, or reputational risk are increasingly unwilling to rely on post-creation verification methods that inherit uncertainty from opaque creation histories. The question they're asking isn't "can we verify this?" but "can we prove how this was created?"
That question requires a different technical foundation. Not watermarks or signatures added after creation, but origin points captured at creation—designed to be tamper-evident, temporally anchored, and independently verifiable. The content that matters most is beginning to arrive with its own unfalsifiable creation history.
The Practical Position
The distinction between verifying what exists and capturing what happened during creation represents the dividing line between organizations that can defend their digital artifacts under scrutiny and those that merely hope their documentation holds up. Forensic-grade thinking isn't a compliance upgrade—it's recognizing that authenticity now requires embedding proof at origin, not layering it afterward.
— Kevin Marsh, Editor-in-Chief
SYNTHETIC PROOF
FROM PROVENANCE TO OPERATIONAL TRUST
Understand Your AI Trust Gap
Synthetic Proof helps teams evaluate verification, provenance, prompt risk, and digital media trust through independent audits and structured findings.
Explore Synthetic ProofSynthetic Proof
Verified — Editorial Layer
This content has passed editorial verification for clarity, accuracy, and trust alignment.
Editor-in-Chief: Kevin Marsh
Verification Status: PASSED
Verification Status: PASSED
Comments
Post a Comment