Critical review showing why statistical models produce false positives and why deterministic provenance is superior. For the past several years, the prevailing strategy for combating synthetic media has been detection: build better classifiers, train on larger datasets, identify artifacts faster than generative models can eliminate them. The logic seemed sound. If AI can create deepfakes, AI can also detect them. Except it hasn't worked. The value of provenance ultimately depends on whether organizations can turn evidence into confident decisions. Synthetic Proof helps examine that broader trust picture across AI content and workflows. Detection-based approaches have reached an operational ceiling. They struggle against modern generative models, degrade rapidly as those models improve, and offer no mechanism to verify authenticity when detection fails. Organizations deploying deepfake detectors today are discovering what researchers have known quietly for s...
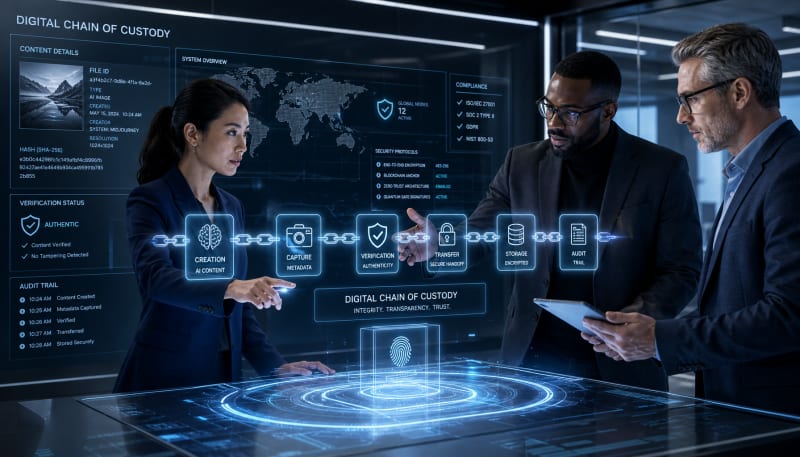
Explore why complete asset histories are becoming essential for trust.
A single AI-generated image can pass through a dozen systems between creation and final publication. It might be generated in one platform, edited in another, stored in a content management system, reviewed by multiple stakeholders, distributed across channels, and eventually embedded in customer-facing materials. At each step, the risk of manipulation, unauthorized modification, or provenance loss increases.
The problem isn't just technical—it's operational. As organizations integrate AI-generated content into production workflows, they're discovering that existing content management practices weren't designed for synthetic media. Without a verifiable record of what happened at each stage, questions about authenticity, compliance, and accountability become impossible to answer with confidence.
As content history becomes a governance concern, organizations need more than another metadata field. Synthetic Proof provides an independent way to assess provenance, verification, and wider AI trust risk.
This is where digital chain of custody becomes essential. Borrowed from legal and forensic contexts, the concept describes a documented trail showing who handled an asset, when, where, and what modifications occurred. For AI content moving through enterprise systems, this trail is becoming a foundational requirement for operational trust.
Why Traditional Content Management Falls Short
Enterprise content systems were built for human-created assets with relatively stable provenance. A photograph has a camera source. A document has an author. These origins are generally fixed and verifiable through metadata embedded at capture.
AI-generated content operates differently. The "source" might be a prompt, a model version, a random seed, or a combination of training data attributes. The asset can be regenerated, modified through additional prompts, or blended with other synthetic elements—all without leaving conventional audit trails.
Version control systems track changes, but they don't verify authenticity. Digital asset management platforms organize files, but they don't cryptographically attest to modification history. Cloud storage provides access logs, but those logs don't prove the integrity of what was stored.
The gap becomes critical when organizations need to answer basic questions: Was this image generated by our approved system? Has it been altered since approval? Can we prove this version is what our compliance team reviewed? Traditional infrastructure doesn't provide definitive answers.
What Digital Chain of Custody Actually Captures
A functional chain of custody for AI content doesn't just track file movement. It creates a cryptographically verifiable record of every substantive event in an asset's lifecycle.
At creation, this means capturing generation parameters—the model used, the prompt or input that produced the output, timestamp, and the generating system's identity. These details establish the asset's origin in a way that can be independently verified later.
During modification, the chain records what changed, who authorized the change, and whether the modification was human-directed or algorithmically applied. This might include editing operations, regeneration with refined prompts, or integration with other content elements.
Distribution events matter as well. When an asset moves between systems, changes format, or gets published to external channels, those transitions become part of the permanent record. If a modified version appears later, the chain reveals whether that modification occurred within authorized workflows or outside them.
Critically, each event in the chain is cryptographically signed and linked to previous events. This creates an immutable record that can't be retroactively altered without detection. The chain itself becomes evidence of integrity—or reveals precisely where integrity was compromised.
The Operational Challenge: Maintaining Custody Across Distributed Systems
Establishing chain of custody for a single asset in a controlled environment is straightforward. The difficulty emerges when AI content flows through real enterprise infrastructure—across departments, cloud services, third-party tools, and external partners.
Content generation might happen in a specialized AI platform. Review and approval might occur in a project management system. Storage might live in a digital asset manager. Publishing might involve multiple distribution channels. Each system operates independently, often with different authentication models, logging capabilities, and metadata standards.
Without intentional design, custody breaks at these boundaries. An asset leaves System A with full provenance metadata. System B imports it as a generic file, stripping context. System C publishes it without any record of where it originated. The chain fragments, and with it, the ability to verify what happened.
This isn't a theoretical concern. Organizations routinely discover AI-generated content in production environments without clear records of approval, modification history, or even confirmation that the content came from authorized generation systems. When incidents occur—copyright disputes, compliance investigations, or authenticity challenges—the absence of documented custody becomes a critical vulnerability.
Integration Points Where Custody Typically Breaks
Export and import operations are common failure points. File formats often don't preserve extended metadata. When an AI-generated image exports as a standard PNG, provenance data embedded in proprietary formats may not survive the conversion.
Human handoffs create documentation gaps. An asset might move from AI operations to marketing to legal review through email, shared drives, or messaging platforms—none of which maintain cryptographic custody records.
Third-party services introduce trust boundaries. When external vendors receive AI content for processing, editing, or distribution, custody depends on their systems documenting their role in the chain. Without standardized approaches, this rarely happens comprehensively.
Building Custody Into Workflows, Not Around Them
Effective chain of custody doesn't function as an add-on audit system. It must integrate directly into content workflows at the points where assets are created, modified, or transferred.
At generation, AI systems should create provenance records as a native part of the output process—not as optional metadata that can be stripped or ignored. This means generation platforms treating custody documentation as essential infrastructure, similar to how version control is fundamental to software development.
During collaboration, tools should propagate custody information automatically. When an asset moves between systems, the receiving system should inherit the existing chain and append its own contribution. This requires either standardized metadata formats or integration layers that translate custody information between platforms.
For distribution, publication systems should verify chain integrity before releasing content. If an asset lacks complete custody documentation or shows signs of unauthorized modification, the system should flag it for review rather than publishing blindly.
This approach shifts custody from a compliance afterthought to an operational enabler. Teams gain visibility into content status, approval state, and modification history as a natural byproduct of working within the system.
What Organizations Need Chain of Custody To Prove
The purpose of maintaining custody isn't documentation for its own sake. It's about answering specific questions that organizations increasingly face with AI-generated content.
Compliance verification: When regulations require disclosure of AI-generated materials, custody records prove what was created by AI versus human contributors. When industry standards mandate approval processes, the chain demonstrates those processes were followed.
Authenticity validation: If content appears in unauthorized contexts or modified forms, custody records establish what the authoritative version was and reveal where divergence occurred. This matters for brand protection, misinformation response, and intellectual property defense.
Risk management: When AI models are updated or deprecated, custody chains identify which published content was generated by affected systems. Organizations can systematically review or replace at-risk assets rather than hoping they've found everything manually.
Operational accountability: When content issues arise—quality problems, policy violations, or unexpected outputs—custody records show exactly what inputs produced the result, which systems were involved, and who authorized publication. This turns vague incidents into specific, actionable findings.
The Infrastructure Gap Between Theory and Practice
The concept of digital chain of custody for AI content is relatively straightforward. The infrastructure to implement it comprehensively is still emerging.
Standardization remains incomplete. While initiatives like C2PA provide frameworks for content credentials, adoption across the full stack of content creation, management, and distribution tools is uneven. Many organizations find themselves building custom integration layers to bridge gaps between systems that don't natively share custody information.
Cryptographic approaches vary. Some systems use blockchain-based records. Others rely on centralized attestation services with cryptographic signing. Still others implement hybrid models. There's no universal consensus on which approach best balances verification strength, performance, privacy, and operational practicality.
Governance models are evolving. Who has authority to append to a custody chain? How are disputes about chain integrity resolved? What happens when a link in the chain involves a system that's been decommissioned? Organizations are developing answers, but industry-wide patterns haven't fully solidified.
The gap creates operational friction. Teams understand they need verifiable custody, but implementing it across heterogeneous infrastructure requires significant integration work, policy development, and sometimes accepting partial coverage while waiting for vendor ecosystem maturity.
Final Thoughts
Digital chain of custody represents a fundamental shift in how organizations should think about AI-generated content. It moves the conversation from "what did we create?" to "can we prove what happened to it?"
This matters because AI content is increasingly indistinguishable from human-created material, increasingly integrated into critical workflows, and increasingly subject to regulatory and reputational scrutiny. Without verifiable custody, organizations operate on trust and hope—adequate when stakes are low, insufficient as AI content scales into production environments.
The technology to maintain comprehensive custody exists. The challenge is operational: integrating chain-of-custody mechanisms into workflows designed before synthetic content became commonplace, establishing governance models that work across organizational boundaries, and building infrastructure that treats provenance as essential rather than optional.
Organizations establishing these capabilities now are building operational advantages that will compound over time. As regulatory expectations tighten and content authenticity becomes a competitive differentiator, the ability to definitively answer questions about AI content origins and handling will separate organizations with mature trust operations from those still operating on assumption.
The Practical Position
The shift from tracking content location to proving content integrity represents a permanent change in how enterprises must think about digital assets. Chain of custody isn't an audit feature—it's the operational foundation that makes AI-generated content governable at scale. Organizations that treat this as infrastructure rather than documentation will define what responsible content distribution actually means.
— Kevin Marsh, Editor-in-Chief
SYNTHETIC PROOF
FROM PROVENANCE TO OPERATIONAL TRUST
Understand Your AI Trust Gap
Synthetic Proof helps teams evaluate verification, provenance, prompt risk, and digital media trust through independent audits and structured findings.
Explore Synthetic ProofSynthetic Proof
Verified — Editorial Layer
This content has passed editorial verification for clarity, accuracy, and trust alignment.
Editor-in-Chief: Kevin Marsh
Verification Status: PASSED
Verification Status: PASSED
Comments
Post a Comment