Learn why organizations are investing in verification instead of detection alone. For years, the fight against synthetic media manipulation followed a familiar pattern: researchers identified deepfake artifacts, built detection models around those signatures, and deployed them across platforms. Detection accuracy improved. Conferences celebrated breakthroughs. The industry felt like it was winning. Then generative AI became exponentially better at eliminating the very artifacts those systems were trained to find. As synthetic media improves, confidence increasingly comes from layered evidence rather than a binary label. Synthetic Proof helps organizations evaluate that evidence in context. What's emerging isn't simply a technical gap that better detection can close. It's a fundamental shift in how organizations must approach digital trust. The old model—detect manipulated content after it's created—assumes defenders can keep pace with attackers....
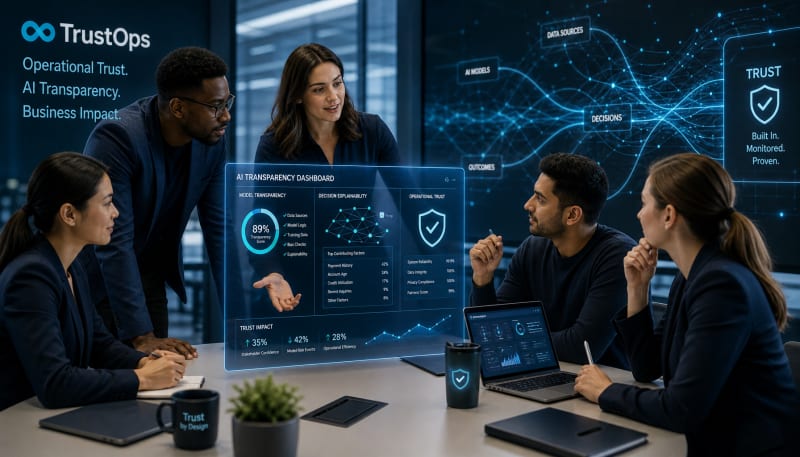
Learn why organizations are operationalizing trust alongside security and DevOps.
Organizations are discovering that transparency isn't the same as trust. A model card documents training data. An audit report catalogs risks. A governance policy outlines principles. Yet when a compliance officer asks whether a specific AI output can be trusted, or when a regulator demands evidence of responsible deployment, these artifacts often fail to answer the operational question that matters most: Can you prove it?
This gap between transparency artifacts and operational trust is driving the emergence of TrustOps—an operational discipline designed to make AI systems continuously verifiable rather than periodically documented. Where traditional AI governance focuses on establishing policies and documenting compliance, TrustOps focuses on creating the infrastructure, processes, and evidence trails that transform those policies into something organizations can operationalize, audit, and defend.
The move from AI policy to operational trust requires independent evidence. Synthetic Proof helps organizations understand where their current trust posture stands.
The distinction matters because AI deployment is moving faster than governance frameworks can accommodate through manual processes alone.
Transparency Creates Documents. TrustOps Creates Evidence.
Most AI transparency efforts produce point-in-time artifacts. A model is evaluated before deployment. A fairness assessment is conducted during development. A risk analysis is completed and filed. These activities are valuable, but they share a fundamental limitation: they describe AI systems at a moment in time rather than creating continuous evidence of how those systems actually behave in production.
TrustOps operates from a different premise. Instead of documenting AI systems periodically, it treats trust as an operational requirement that must be maintained, measured, and verified throughout the entire lifecycle of an AI system. That means capturing structured evidence about inputs, outputs, decisions, and changes—not as an occasional governance exercise, but as a continuous operational capability.
The shift is similar to how DevOps transformed software deployment. Before DevOps, organizations released software in carefully planned cycles with extensive documentation. DevOps didn't eliminate planning or documentation—it made deployment continuous and created the infrastructure to support that continuity. TrustOps does something similar for AI governance. It doesn't replace policies or principles. It creates the operational layer that makes those policies enforceable in systems that generate thousands or millions of outputs daily.
The Operational Questions That Governance Documents Can't Answer
Consider the questions organizations increasingly face when deploying AI systems in regulated environments, high-stakes applications, or customer-facing contexts:
Which version of which model generated this specific output? What inputs were used? Has this model been modified since approval? Can you prove this content originated from your system and not another source? Can you demonstrate that your AI system is operating within the boundaries your governance framework established?
These aren't theoretical questions. They appear in regulatory inquiries, customer disputes, internal audits, and security investigations. They require specific, verifiable evidence about individual AI interactions—not general descriptions of how systems are designed to work.
Traditional governance artifacts struggle with these questions because they're built for assessment rather than verification. A model card describes training data composition but doesn't prove which model version produced a disputed output. An audit report evaluates risk levels but doesn't create a tamper-evident record of production behavior. A fairness assessment measures bias during testing but doesn't verify fairness for individual decisions made months later.
TrustOps addresses this gap by treating verification as an operational requirement from the beginning. That means capturing structured metadata about AI interactions, maintaining cryptographic proof of authenticity, creating audit trails that can withstand scrutiny, and building infrastructure that makes these capabilities practical at scale.
From Periodic Audits to Continuous Verification
One of the most significant shifts TrustOps introduces is the move from periodic compliance checks to continuous verification infrastructure. In traditional governance models, organizations assess AI systems at deployment and then periodically thereafter—quarterly reviews, annual audits, or compliance checks triggered by specific events.
This approach made sense when AI systems were relatively static and deployment was carefully controlled. It breaks down when organizations operate dozens or hundreds of AI workflows that change frequently, interact with dynamic data sources, and generate outputs that immediately affect business operations or customer experiences.
Continuous verification doesn't mean constant manual review. It means building systems that automatically capture the evidence needed to answer trust questions whenever they arise. Which prompts were used. Which model versions were active. What transformations were applied to inputs. How outputs were generated and delivered. Whether configurations remained within approved parameters.
This evidence becomes the foundation for both proactive governance and reactive investigation. Proactively, it enables organizations to monitor AI systems for drift, anomalies, or policy violations in near real-time. Reactively, it provides the detailed trail needed to investigate specific incidents, respond to audits, or defend decisions under scrutiny.
The Infrastructure Layer Organizations Are Building
TrustOps requires infrastructure that most organizations don't currently have. That infrastructure typically includes several interconnected capabilities:
Provenance capture creates structured records of how AI outputs were produced—tracking model versions, input sources, processing steps, and configuration parameters throughout the generation lifecycle. This isn't logging in the traditional sense. It's the creation of verifiable metadata that establishes the origin and history of AI-generated content.
Cryptographic attestation provides tamper-evident proof that specific outputs came from specific systems under specific conditions. This addresses a growing problem: as AI-generated content becomes ubiquitous, organizations need ways to prove authenticity and prevent manipulation of both outputs and the records that describe them.
Policy enforcement mechanisms translate governance frameworks into technical controls that operate continuously rather than periodically. Instead of reviewing AI system behavior against policies after the fact, TrustOps infrastructure enforces boundaries, triggers alerts, and blocks non-compliant operations as they occur.
Verification interfaces make evidence accessible to stakeholders who need it—compliance teams, auditors, customers, regulators—without exposing sensitive system details or creating unmanageable operational overhead.
These capabilities are beginning to coalesce into what some organizations are calling "trust infrastructure"—a dedicated layer that sits between AI systems and the governance frameworks meant to guide them.
Who Needs TrustOps, and When
Not every AI application requires the operational rigor that TrustOps provides. Organizations using AI for internal experimentation, low-stakes recommendations, or tightly controlled environments may find that traditional documentation and periodic audits remain sufficient.
TrustOps becomes essential when organizations face specific operational pressures. Regulatory scrutiny that demands evidence of specific AI decisions. Customer-facing applications where disputes about AI-generated outputs carry legal or reputational risk. High-stakes domains like healthcare, finance, or legal services where decisions must be defensible. Situations where AI systems operate with significant autonomy and insufficient transparency creates compliance or security exposure.
The discipline is also becoming relevant as organizations scale AI deployment beyond a handful of carefully monitored systems. Managing trust for five AI models through manual governance processes is one thing. Managing trust for fifty models across multiple teams, geographies, and use cases requires operational infrastructure that makes verification practical rather than heroic.
Early adoption is appearing in sectors that face both regulatory pressure and operational complexity—financial services firms deploying AI for credit decisions, healthcare organizations using AI for diagnostic support, enterprises in regulated industries where AI-generated content creates compliance obligations, and platforms where user-generated AI content creates new authenticity and provenance challenges.
The Discipline Is Still Taking Shape
TrustOps remains an emerging discipline rather than an established standard. Organizations are building these capabilities through a combination of custom infrastructure, adapted DevOps tooling, and purpose-built trust platforms. Standards are evolving. Best practices are being discovered rather than codified. The boundary between what constitutes "good enough" governance and what requires dedicated TrustOps infrastructure is still being defined through practical experience.
What's becoming clear is that the gap between transparency and operational trust won't close through documentation alone. As AI systems become more capable, more autonomous, and more deeply embedded in business operations, the ability to continuously verify their behavior stops being a nice-to-have governance enhancement and starts being a fundamental operational requirement.
Organizations that recognize this shift early are building the infrastructure and processes that will allow them to deploy AI systems with both confidence and accountability. Those that treat trust as something that can be documented periodically rather than verified continuously may find themselves unable to answer the operational questions their stakeholders, regulators, and customers increasingly expect them to address.
Final Thoughts
TrustOps represents a fundamental reframing of how organizations approach AI governance—from periodic assessment to continuous verification, from documentation to evidence, from principles to operational infrastructure. It doesn't replace traditional governance frameworks. It creates the operational layer that makes those frameworks enforceable in environments where AI systems generate thousands of decisions daily and where the question "Can you prove it?" demands more than a policy document or an audit report.
The organizations building these capabilities now aren't necessarily more risk-averse than their peers. They've simply recognized that AI transparency and AI trust solve different problems—and that the gap between them grows wider as AI deployment accelerates. TrustOps is how that gap gets closed.
The Practical Position
Organizations deploying AI at scale are learning that periodic assessments can't answer real-time verification questions. TrustOps reflects a fundamental shift: trust is becoming infrastructure, not documentation. The organizations building continuous verification capabilities today are establishing the operational foundation that tomorrow's regulatory environment will assume already exists. Trust delayed is trust denied.
— Kevin Marsh, Editor-in-Chief
SYNTHETIC PROOF
TURN TRUST INTO AN OPERATIONAL CAPABILITY
Evaluate Where Trust Breaks Down
Synthetic Proof helps teams identify trust gaps across prompts, digital media, verification practices, and emerging AI workflows.
Assess Your Trust ReadinessSynthetic Proof
Verified — Editorial Layer
This content has passed editorial verification for clarity, accuracy, and trust alignment.
Editor-in-Chief: Kevin Marsh
Verification Status: PASSED
Verification Status: PASSED
Comments
Post a Comment