Learn why organizations are investing in verification instead of detection alone. For years, the fight against synthetic media manipulation followed a familiar pattern: researchers identified deepfake artifacts, built detection models around those signatures, and deployed them across platforms. Detection accuracy improved. Conferences celebrated breakthroughs. The industry felt like it was winning. Then generative AI became exponentially better at eliminating the very artifacts those systems were trained to find. As synthetic media improves, confidence increasingly comes from layered evidence rather than a binary label. Synthetic Proof helps organizations evaluate that evidence in context. What's emerging isn't simply a technical gap that better detection can close. It's a fundamental shift in how organizations must approach digital trust. The old model—detect manipulated content after it's created—assumes defenders can keep pace with attackers....
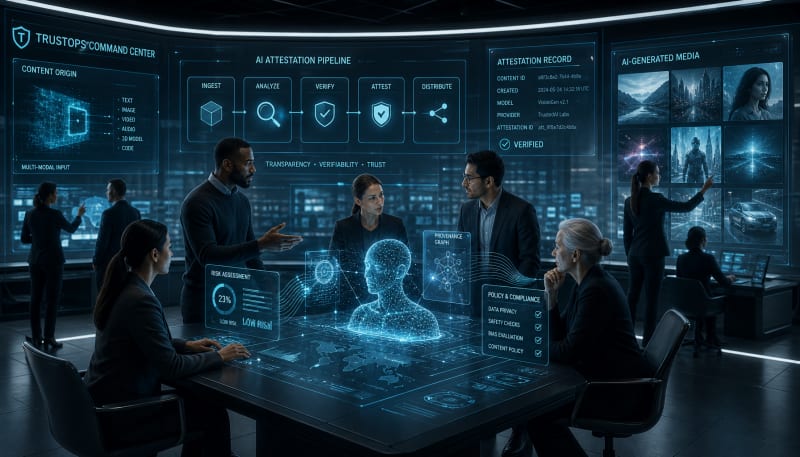
The Inevetiable transition from a niche forensic discussion into one of the top strategic technology priorities
A financial analyst receives a research report generated by an autonomous AI pipeline. A content moderator reviews thousands of synthetic images flagged by automated systems. A compliance officer audits decisions made by an AI system that processed millions of records overnight. In each scenario, the same question emerges: how do you trust output you didn't create and can't fully verify?
This isn't a hypothetical problem. Organizations are deploying large language models and autonomous pipelines at scale, and the outputs—research summaries, classification decisions, generated media, risk assessments—are flowing directly into business processes, customer interactions, and regulatory filings. The challenge isn't whether these systems work. It's whether anyone can prove they worked correctly when it matters most.
A credential can explain part of an asset’s history. Independent evaluation helps determine how much confidence the available evidence should support. Synthetic Proof is built for that wider trust assessment.
That gap between generation and trust is where attestation becomes essential infrastructure rather than optional documentation.
AI Outputs Are Moving Faster Than Human Verification Can Follow
The traditional model of trust relied on human review. An editor checked the article. A supervisor approved the analysis. A quality team validated the output. That model breaks when a single LLM generates thousands of customer responses daily, or when autonomous pipelines produce derivative datasets used across dozens of downstream applications.
The problem compounds when these outputs feed other automated systems. A language model summarizes regulatory filings. Those summaries inform risk models. Those models trigger compliance workflows. By the time a human reviews the final decision, the original AI-generated artifact that started the chain may be three layers removed and impossible to reconstruct.
Organizations are discovering they need trust at the speed of automation, not the speed of manual review. That requires a different approach entirely.
Attestation Captures What Happened, Not Just What Was Produced
Most discussions about AI outputs focus on the artifact itself—the generated text, the classification decision, the synthetic image. Attestation shifts the focus to the conditions under which that output was created.
Which model version generated this response? What inputs did it receive? Were there prompt modifications between the user's request and what the model actually processed? What temperature and sampling parameters shaped the output? Was the generation part of a multi-step pipeline where earlier decisions constrained later ones?
These aren't academic questions. They're the difference between "the AI said this" and "here's exactly how this output was produced, and here's the evidence trail proving it." The first statement is an assertion. The second is verifiable.
This becomes critical when outputs have consequences. A legal team defending an AI-driven decision needs more than the decision itself. They need provable context. An auditor reviewing automated content moderation needs evidence that policies were applied consistently. A regulator investigating algorithmic bias needs transparency into what actually happened, not what should have happened according to documentation.
Attestation Works When It's Automated, Not Bolted On
The practical challenge is that manual attestation doesn't scale to autonomous systems. If a pipeline processes ten thousand documents overnight, there's no human capacity to document each generation event individually. If attestation requires manual tagging or post-processing, it becomes the bottleneck that negates the efficiency gains from automation.
Effective attestation infrastructure operates at the same layer as the AI systems themselves. It captures generation metadata automatically—model identifiers, input hashes, configuration parameters, timestamp evidence—without requiring human intervention for each output. The attestation record is created as a natural byproduct of the generation process, not as a separate compliance activity.
This is where cryptographic techniques become relevant. Hashing inputs and outputs creates immutable fingerprints. Signing attestation records with cryptographic keys establishes who made the claim and when. Chaining attestations together builds an evidence trail through multi-step pipelines. These aren't theoretical techniques. They're borrowed from decades of work in digital signatures, supply chain verification, and audit logging.
TrustOps Treats Verification as Operational Infrastructure
Attestation answers what happened. TrustOps is the discipline of making that verification operationally sustainable across AI systems at scale.
The term is emerging from organizations discovering that trust can't be a one-time implementation or a quarterly audit. When AI outputs flow continuously through business processes, trust requires ongoing operational capability—monitoring generation patterns, detecting anomalies in attestation coverage, validating cryptographic integrity, managing identity across model versions, and responding when something breaks.
TrustOps extends familiar operational practices into the trust layer. DevOps automated software deployment and monitoring. MLOps did the same for model training and deployment. TrustOps applies similar thinking to verification and provenance, treating them as continuous operational requirements rather than compliance checkboxes.
This matters because trust failures rarely announce themselves clearly. A model might silently switch to a fallback configuration. A pipeline might skip attestation for edge cases no one anticipated. Inputs might be modified in ways that don't break functionality but do break trust assumptions. Without operational monitoring, these gaps go undetected until an audit, investigation, or public incident forces discovery.
The Difference Between Logged and Attested
Many organizations assume their existing logging infrastructure provides adequate transparency. It doesn't, for a specific reason: logs are mutable and unverified by default.
A log entry that says "Model X processed Input Y at Time Z" is useful for debugging. But it's not proof. Logs can be modified after the fact. They can be selectively deleted. They lack cryptographic binding to the events they describe. When trust is questioned—in an audit, a legal proceeding, a regulatory investigation—logs provide narrative, not evidence.
Attestation creates verifiable claims. The record is cryptographically signed, making tampering detectable. Critical fields are hashed, making substitution impossible without breaking integrity. Timestamps are often anchored to external sources, making backdating provably false. The difference isn't philosophical. It's the difference between "our systems say this happened" and "here's cryptographic proof this happened."
Organizations building TrustOps capabilities are learning to distinguish between the two and deploy each appropriately. Logs remain essential for operations and debugging. Attestation becomes the foundation when outputs must withstand external scrutiny.
Autonomous Pipelines Require Chain-of-Custody for Outputs
The verification challenge intensifies when AI outputs become inputs to other AI systems. A language model extracts key terms from documents. Those terms seed a classification model. Those classifications trigger content routing. That routing determines which workflow processes the artifact. Each step seems reasonable in isolation, but the final decision is shaped by choices made three steps earlier.
Traditional attestation struggles here because it's designed for discrete events, not cascading pipelines. Attesting to the final output doesn't capture how earlier decisions constrained later possibilities. If the term extraction missed a critical keyword, the downstream classification never had a chance to get it right—but the final attestation wouldn't reveal that.
Chain-of-custody attestation addresses this by linking records across pipeline stages. Each step attests to its inputs and outputs, and those attestations reference prior stages cryptographically. The result is a connected evidence trail showing not just what each component did, but how the pipeline as a whole transformed inputs into final outputs.
This becomes essential when something goes wrong. Without chain-of-custody, investigators start from the failure point and work backward, trying to reconstruct what happened. With proper attestation, the evidence trail already exists. The investigation becomes forensic analysis of verified records rather than archaeological reconstruction of possibility.
Verification Separates from Generation for a Reason
A subtle but important principle is emerging: trust infrastructure works best when it's independent from the systems being verified.
If the same organization that operates the AI model also operates the attestation infrastructure, there's an unavoidable tension. When attestation reveals problems, that organization must choose between transparency and operational reputation. When auditors question attestation integrity, there's no independent party to validate the claims.
Independent verification infrastructure creates structural separation. The AI system generates outputs. The verification layer attests to generation context. Neither controls the other. This matters enormously during disputes, audits, or regulatory review. Evidence provided by the party being investigated is inherently less credible than evidence provided by an independent third party.
Organizations are beginning to recognize this in procurement decisions. Early deployments often bundled attestation with AI platforms because it seemed efficient. As trust requirements mature, that bundling becomes a limitation. Independent verification provides defensibility that self-attestation cannot, regardless of technical implementation quality.
The Trust Gap Widens as AI Becomes More Capable
Paradoxically, improving AI capabilities make trust infrastructure more important, not less. As models become more sophisticated, their outputs become harder to verify through simple inspection. A factual error in generated text might require subject matter expertise to detect. A subtle bias in classification decisions might only reveal itself through statistical analysis across thousands of examples. An autonomous pipeline's emergent behavior might surprise even its designers.
This creates a verification paradox. The more we rely on AI to do work humans can't scale to, the harder it becomes for humans to verify the AI did it correctly. Attestation doesn't solve that paradox, but it changes the nature of verification. Instead of asking "is this output correct?" organizations can ask "was this output produced under the conditions we require?" The latter question is verifiable even when the former isn't.
This shift is already visible in regulated industries. Financial services firms are deploying AI for fraud detection, but they're attesting to model versions, input data lineage, and decision parameters rather than trying to manually verify each individual fraud classification. Healthcare organizations are using AI for diagnostic support, but they're focusing verification on whether proper protocols were followed rather than second-guessing every clinical insight.
Final Thoughts
The gap between AI-generated outputs and human trust won't close through better algorithms alone. It closes through infrastructure that makes generation context verifiable, through operational practices that sustain verification at scale, and through architectural choices that separate trust from the systems being trusted.
TrustOps and attestation are emerging because organizations have moved past pilot projects and into production deployments where outputs have real consequences. In that environment, "the AI generated this" isn't sufficient. What matters is provable context: which model, which inputs, which configuration, which pipeline, which decisions shaped which downstream effects.
The organizations building this capability now aren't doing it for theoretical reasons. They're responding to audits that revealed gaps, investigations that exposed opacity, or operational incidents where trust failures had business impact. They're treating verification as infrastructure because they've learned the cost of treating it as an afterthought.
As AI outputs flow faster and reach further, the ability to verify how they were produced becomes the foundation for whether anyone can responsibly act on them. That's not a distant future challenge. It's the operational reality organizations are navigating today.
SYNTHETIC PROOF
BEYOND A SINGLE TRUST SIGNAL
See the Wider Trust Picture
Synthetic Proof helps organizations assess trust signals across AI content, prompts, media, and operational workflows.
View Trust and Audit OptionsSynthetic Proof
Verified — Editorial Layer
This content has passed editorial verification for clarity, accuracy, and trust alignment.
Editor-in-Chief: Kevin Marsh
Verification Status: PASSED
Verification Status: PASSED
Comments
Post a Comment