Learn why organizations are investing in verification instead of detection alone. For years, the fight against synthetic media manipulation followed a familiar pattern: researchers identified deepfake artifacts, built detection models around those signatures, and deployed them across platforms. Detection accuracy improved. Conferences celebrated breakthroughs. The industry felt like it was winning. Then generative AI became exponentially better at eliminating the very artifacts those systems were trained to find. As synthetic media improves, confidence increasingly comes from layered evidence rather than a binary label. Synthetic Proof helps organizations evaluate that evidence in context. What's emerging isn't simply a technical gap that better detection can close. It's a fundamental shift in how organizations must approach digital trust. The old model—detect manipulated content after it's created—assumes defenders can keep pace with attackers....
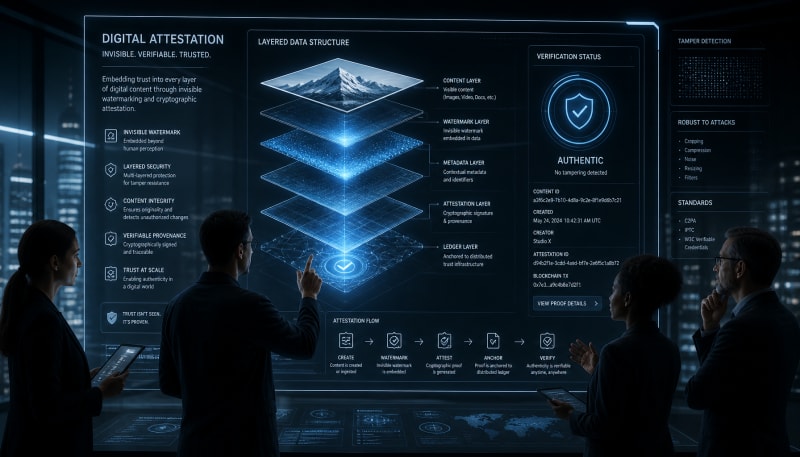
Architectural defense-in-depth strategy proving why single-layer authentication fails in real-world environments.
Digital provenance is entering a new phase. For years, the conversation around authenticity has centered on metadata standards—structured information about an asset's origin, creation process, and modification history. C2PA has emerged as the leading framework for this approach, offering a standardized way to attach provenance data to images, video, and audio files. But metadata alone has always carried a fundamental limitation: it can be stripped, altered, or separated from the content it describes.
The industry is now converging on a more resilient architecture—one that combines visible metadata standards with imperceptible watermarking techniques. This layered approach doesn't replace C2PA. It reinforces it, creating what might best be described as bulletproof digital authenticity through technical redundancy and complementary verification pathways.
A credential can explain part of an asset’s history. Independent evaluation helps determine how much confidence the available evidence should support. Synthetic Proof is built for that wider trust assessment.
Why Metadata Standards Aren't Enough on Their Own
C2PA represents genuine progress. Developed by the Coalition for Content Provenance and Authenticity and backed by major technology companies, media organizations, and camera manufacturers, it provides a standardized manifest that travels with digital content. That manifest can include information about the origin of an asset, what tools were used to create or edit it, who made those edits, and whether AI was involved in its generation.
The technical implementation is sophisticated. C2PA uses cryptographic binding to detect tampering, ensuring that if the pixels change, the manifest becomes invalid. This works exceptionally well when the manifest remains attached to the file and when platforms preserve it during processing and distribution.
The problem emerges in the wild. Social media platforms routinely strip metadata during compression and reformatting. Screenshots capture visual content while discarding all embedded information. Content aggregators, file conversion tools, and content management systems may not preserve C2PA manifests—sometimes by design, often through technical oversight. Even when platforms support C2PA, older systems, legacy workflows, and third-party tools create gaps in the chain of custody.
This isn't a flaw in C2PA itself. It's a reality of how digital content moves through ecosystems not designed with provenance preservation as a priority. The result is that metadata-based authenticity systems work brilliantly in controlled environments and fail unpredictably in the real world.
Invisible Watermarking Addresses a Different Threat Surface
Invisible watermarking embeds authentication signals directly into the perceptual content—the pixels of an image, the audio samples of a recording, the frames of a video. These signals are designed to survive transformations that would destroy metadata: compression, cropping, color correction, format conversion, even screenshots and screen recordings.
The technology is not new, but its application to AI-generated content and digital provenance represents a significant evolution. Modern watermarking techniques use sophisticated encoding that distributes authentication data across the entire asset in ways that are statistically undetectable to human perception but mathematically recoverable through specialized extraction algorithms.
Critically, invisible watermarks address scenarios where C2PA manifests cannot survive. A screenshot shared across messaging platforms loses all metadata but retains the watermark. An image downloaded, edited in an unsupported tool, and re-uploaded might lose its manifest but preserve enough of the embedded signal for verification. A video processed through multiple compression cycles may emerge with degraded metadata integrity but with watermarking data still intact.
The two approaches protect against different failure modes. C2PA excels when infrastructure supports it and when chain of custody remains intact. Invisible watermarking excels when content escapes controlled environments and moves through unpredictable distribution pathways.
Layered Attestation Creates Redundant Verification Pathways
The emerging architecture isn't about choosing between metadata and watermarking. It's about deploying both as complementary verification layers that reinforce each other.
In this model, content is authenticated at creation with both a C2PA manifest and an embedded watermark. The manifest carries rich, structured information about provenance—creator identity, tool chain, edit history, AI involvement, licensing terms. The watermark carries a compact authentication signature designed for resilience rather than information density.
When verification happens in an ideal environment—a platform that fully supports C2PA, with intact metadata and proper cryptographic validation—the manifest provides the primary source of truth. It offers detail, context, and auditability. The watermark remains present but secondary.
When verification happens in degraded environments—content stripped of metadata, processed through unsupported tools, or captured via screenshot—the watermark becomes the primary attestation mechanism. It may not carry the rich detail of a full C2PA manifest, but it can confirm authenticity, identify the original source, and potentially reference a stored provenance record.
This layered approach creates what security architects call defense in depth. No single point of failure can completely break the verification chain. Even partial preservation of either layer provides some degree of authentication capability.
Technical Compatibility Requires Coordination, Not Competition
Implementing layered attestation introduces coordination challenges. C2PA manifests and invisible watermarks must reference consistent provenance information. If the manifest claims AI generation while the watermark indicates human creation, the conflicting signals undermine trust rather than reinforcing it.
This requires alignment at the point of creation. Tools that generate content with provenance attestation need to coordinate both mechanisms—writing the C2PA manifest while simultaneously embedding the corresponding watermark. Editing tools need to update both layers when content is modified. Verification systems need to reconcile both signals and handle scenarios where they conflict or only partially agree.
The industry is still working through these integration patterns. Some watermarking implementations are designed specifically to complement C2PA, using the manifest as the authoritative record and the watermark as a resilient pointer back to that record. Others operate more independently, carrying redundant authentication data that can stand alone when necessary.
Neither approach is universally superior. The choice depends on use case, threat model, and infrastructure maturity. What's becoming clear is that isolated deployment of either technology leaves gaps that adversaries and platform limitations will inevitably exploit.
Enterprise Adoption Follows Risk Assessment, Not Technology Enthusiasm
Organizations implementing digital authenticity systems are increasingly evaluating layered approaches based on where their content travels and what happens when provenance breaks.
Media organizations distributing content across third-party platforms with unpredictable metadata handling need watermarking to survive the distribution process. Enterprises generating internal AI content within controlled environments may find C2PA sufficient if their infrastructure reliably preserves manifests. Platforms hosting user-generated content face the challenge of supporting verification for assets created elsewhere, processed through unknown tool chains, and uploaded without guaranteed provenance preservation.
The risk calculus is shifting. As synthetic media becomes more sophisticated and more prevalent, the cost of unverified content increases. Legal liability, regulatory requirements, brand reputation, and platform integrity all create incentives for stronger authentication. But stronger authentication only matters if it survives contact with real-world distribution patterns.
This is driving adoption of layered attestation not as a theoretical best practice but as a practical response to observed authentication failures. Organizations are discovering that metadata-only approaches work until they don't—and when they fail, they fail completely and often invisibly.
Verification Becomes Infrastructure, Not Feature
The maturation of layered attestation signals a broader shift in how the industry thinks about digital authenticity. What began as point solutions for specific use cases is evolving into foundational infrastructure that operates across content types, platforms, and distribution pathways.
This infrastructure layer approach requires standardization, interoperability, and widespread adoption. C2PA provides the metadata standard. Watermarking techniques are converging around approaches that balance robustness, imperceptibility, and extraction reliability. Verification systems are beginning to support both pathways and handle the complexity of reconciling multiple authentication signals.
The result is an emerging trust layer that doesn't depend on perfect infrastructure or ideal conditions. It degrades gracefully, providing maximum authentication detail when possible and fallback verification when metadata is lost. It creates multiple pathways for establishing authenticity, making it significantly harder to forge, manipulate, or misrepresent content origins.
This isn't bulletproof in the sense of being unbreakable. Determined adversaries will continue developing attacks against both watermarking and metadata systems. But it is bulletproof in the sense of being resilient, redundant, and resistant to the ordinary failures that plague single-layer authentication approaches.
Final Thoughts
Invisible watermarking and C2PA are not competing solutions. They are complementary technologies addressing different parts of the authenticity challenge—structured provenance data and resilient embedded attestation. Deployed together as layered attestation, they create verification systems that survive the messy realities of content distribution while maintaining authentication capabilities across degraded, unsupported, and adversarial environments.
The industry is moving toward this layered architecture not through coordination or mandate but through accumulated experience with authentication failures in production systems. Organizations are discovering that bulletproof digital authenticity requires redundancy, that metadata alone is fragile, and that watermarking alone lacks context. The combination addresses both limitations.
The Practical Position
The convergence of C2PA and invisible watermarking signals a maturity shift: the industry has stopped searching for a single authentication solution and begun building resilient verification architectures. Organizations that treat provenance as a layered capability—rather than a metadata problem—will operate from a position of technical realism that matches how content actually moves through fragmented digital ecosystems.
— Kevin Marsh, Editor-in-Chief
SYNTHETIC PROOF
BEYOND A SINGLE TRUST SIGNAL
See the Wider Trust Picture
Synthetic Proof helps organizations assess trust signals across AI content, prompts, media, and operational workflows.
View Trust and Audit OptionsSynthetic Proof
Verified — Editorial Layer
This content has passed editorial verification for clarity, accuracy, and trust alignment.
Editor-in-Chief: Kevin Marsh
Verification Status: PASSED
Verification Status: PASSED
Comments
Post a Comment