Managing Execution Limits, Tool Scoping, and Delegated Authority in Multi-Agent Workflows Agentic AI systems—agents capable of planning, reasoning, and taking action with minimal human supervision—are moving from research labs into production environments. Unlike traditional AI models that generate text or images on demand, these agents interact with tools, execute commands, access databases, and modify digital assets. When multiple agents operate within the same environment, the governance challenge intensifies significantly. The principle of least-privilege access, a cornerstone of information security for decades, has never been more relevant—or more difficult to implement. In multi-agent systems, determining which agents should access which tools, under what conditions, and with what level of authority requires a fundamental rethinking of access control architectures. Related: If your workflow touches verification, provenance, or suspicious media, Synthetic...
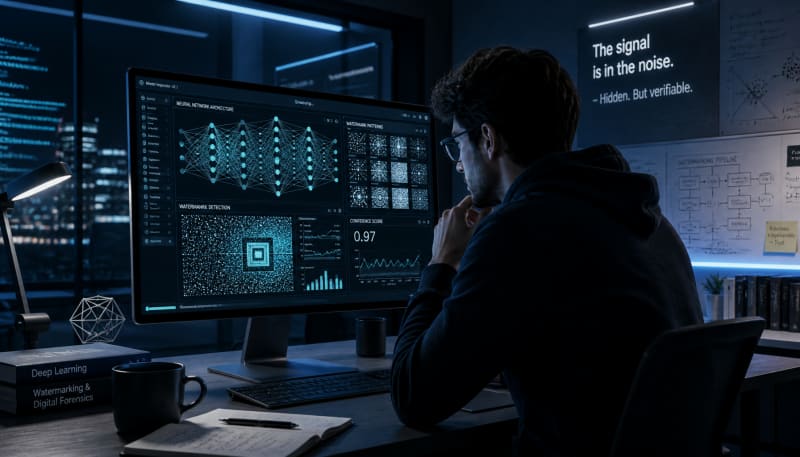
Why modern generative models are using latent-space watermarks to identify synthetic media.
A high-resolution image generated by an AI model looks identical to a photograph. A synthetic audio clip sounds exactly like a human voice. A video created entirely by generative models passes visual inspection. The content is indistinguishable—until it needs to be verified.
This is the authenticity problem facing every organization deploying generative AI at scale. Traditional metadata can be stripped in seconds. Visible watermarks can be cropped out. File hashes break the moment content is edited or compressed. The industry needs a form of provenance that survives transformation, resists tampering, and remains invisible to users while being detectable by verification systems.
Standards can make content more transparent without eliminating every operational risk. Synthetic Proof helps teams examine trust across the full workflow rather than relying on one signal alone.
Invisible AI watermarking embeds authenticity signals directly into the neural network's generation process—not as an afterthought applied to finished content, but as an intrinsic part of how the model produces output. It's a fundamentally different approach to provenance, and it's quietly reshaping how the AI industry thinks about trust.
The Signal Lives in the Model, Not the Metadata
Traditional content authentication relies on external markers. A signature in a file header. A hash recorded in a database. A visible logo burned into an image corner. These methods treat provenance as something attached to content after creation.
Invisible watermarking works differently. The signal is embedded during generation—woven into pixel values, token distributions, or audio waveforms as the model produces output. This happens at inference time, meaning every piece of content created by a watermarked model carries the signal automatically.
The watermark isn't stored separately. It's not metadata that can be removed. It exists as a subtle statistical pattern within the content itself—imperceptible to human observers but mathematically detectable by verification systems that know what to look for.
For images, this might mean adjusting color values or texture patterns in ways that don't affect visual quality. For text, it might involve biasing token selection probabilities during generation to create a detectable signature. For audio, it could mean embedding patterns in frequency domains that remain inaudible but survive compression and format conversion.
The technical challenge isn't just making the signal invisible. It's making it robust—ensuring it persists through editing, compression, format changes, and partial cropping while remaining undetectable to users and resistant to removal by adversaries who know it exists.
Neural Networks Learn to Embed and Detect Simultaneously
The most sophisticated watermarking systems train two neural networks in parallel: one that embeds signals during content generation, and one that extracts and verifies those signals from finished content.
During training, the embedding network learns to introduce patterns that survive common transformations. The detection network learns to recognize those patterns even after the content has been compressed, resized, or partially modified. The two networks improve together—the embedding network gets better at creating robust signals, while the detection network gets better at finding them under degraded conditions.
This approach allows watermarking to adapt to the specific properties of different content types. Image watermarks can be optimized for visual imperceptibility and resilience to JPEG compression. Text watermarks can be designed to survive paraphrasing or translation. Audio watermarks can be tuned to remain detectable after transcoding or noise addition.
Some implementations use adversarial training—deliberately trying to remove or corrupt the watermark during training so the system learns to resist those attacks in production. The embedding network learns to place signals in parts of the content that are hardest to alter without degrading quality.
The result is a watermarking system that isn't simply stamping a signature onto content. It's learning the optimal way to encode authenticity information within the natural variation already present in that content type.
Robustness Is the Engineering Challenge
A watermark that disappears the moment someone edits the content isn't useful for real-world verification. Robustness—the ability to survive transformation—determines whether invisible watermarking becomes infrastructure or remains a research curiosity.
Images get resized, compressed, filtered, and cropped. Text gets paraphrased, summarized, or translated. Audio gets converted between formats, compressed to reduce file size, or mixed with other sounds. Any of these operations can destroy fragile watermarks.
Organizations deploying watermarked models need the signal to persist through workflows where content is edited, repurposed, and transformed multiple times before publication. A marketing team might generate an image, resize it for different platforms, add text overlays, adjust colors, and compress it for web delivery. The watermark needs to survive that entire pipeline.
This is why watermarking systems are evaluated not just on imperceptibility but on detection rates after transformation. Can the signal be recovered from a heavily compressed JPEG? From a screenshot of the original image? From a video frame that was re-encoded three times?
Different use cases have different robustness requirements. A newsroom verifying the source of a submitted image needs watermarks that survive aggressive editing. A platform detecting AI-generated spam needs signals that persist even when adversaries actively try to remove them. A creative studio tracking asset provenance internally needs reliability more than attack resistance.
The engineering tension is always between robustness and imperceptibility. Stronger signals survive more transformations but risk becoming detectable. Subtle signals remain invisible but may not survive real-world content workflows. Finding that balance is where the technical sophistication lives.
Detection Requires Access to the Verification System
Embedding a watermark is only half the system. Detecting it requires a trained verification model—and increasingly, organizations are realizing that who controls detection infrastructure determines who controls trust.
Some watermarking approaches are proprietary. The model vendor embeds signals using their own method, and only their verification system can detect them. This creates dependency: organizations using those models must rely on the vendor's detection infrastructure to verify their own content.
Other approaches aim for open standards. The Coalition for Content Provenance and Authenticity (C2PA) and similar initiatives are working toward interoperable watermarking where multiple vendors can embed signals that conform to shared specifications, and multiple verification systems can detect them.
The industry tension here mirrors larger questions about trust infrastructure. Should provenance verification be controlled by the companies that create generative models? Should it be managed by independent third parties? Should it be built as open-source public infrastructure?
For enterprises, this isn't just a technical question. It's a governance question. If your content verification depends on a vendor's proprietary detection system, what happens if that vendor changes pricing, shuts down the service, or gets acquired? If you're building compliance workflows around AI-generated content, can you rely on external detection infrastructure you don't control?
This is pushing some organizations toward platforms that provide independent watermark verification—systems that can detect signals from multiple model providers and give organizations consistent detection capabilities regardless of where their content originated.
Watermarking Moves From Optional to Expected
Two years ago, invisible watermarking was a research topic discussed in academic papers. Today, it's becoming a baseline expectation for any generative model deployed in regulated environments or public-facing applications.
Regulatory pressure is accelerating adoption. The EU AI Act includes provisions around transparency and traceability for generative AI systems. California's proposed AI disclosure laws would require labeling of synthetic media in certain contexts. Newsrooms and social platforms are implementing policies that require provenance signals for AI-generated content.
Model providers are responding. OpenAI has experimented with text watermarking approaches. Google DeepMind released SynthID, a watermarking system for images and audio. Other providers are building similar capabilities or partnering with third-party verification platforms.
But widespread adoption faces practical obstacles. Not all models are watermarked yet. Not all watermarking methods are equally robust. There's no universal standard for detection. Organizations can't assume that AI-generated content they encounter will carry detectable provenance signals.
This creates a transitional period where some content is verifiable and some isn't. Where some platforms require watermarking and others don't. Where verification is possible for some content types but not others. Enterprises navigating this landscape need verification strategies that work in a partially watermarked world—combining watermark detection with other provenance signals when native watermarks aren't present.
The Architecture Is Shifting Toward Verification Layers
Invisible watermarking isn't replacing other forms of provenance—it's becoming one layer in a broader verification architecture.
Organizations are building systems where watermark detection works alongside cryptographic signatures, metadata standards like C2PA, model output analysis, and behavioral provenance tracking. When a watermark is present and detectable, it provides strong native signal. When it's not, other verification methods fill the gap.
This layered approach reflects a practical reality: no single provenance technology works in every situation. Watermarks can be removed by determined adversaries. Metadata can be stripped. Cryptographic signatures require key management. Behavioral analysis produces probabilistic rather than definitive results.
The most resilient verification systems use multiple signals and degrade gracefully when some aren't available. They might prefer watermark detection when possible, fall back to metadata verification when watermarks aren't present, and use statistical analysis as a final layer when neither is available.
For enterprises, this means provenance infrastructure needs to be designed for heterogeneity. Your verification system should work with content from multiple model providers using different watermarking approaches. It should handle content that predates watermarking or comes from sources that don't implement it. It should provide consistent verification workflows even as the underlying signal landscape changes.
Final Thoughts
Invisible AI watermarking represents a fundamental shift in how authenticity signals are attached to synthetic content. Rather than applying provenance after creation, it embeds verification into the generation process itself—making authenticity intrinsic rather than supplemental.
The technology is moving rapidly from research to production. Model providers are implementing watermarking. Regulatory frameworks are beginning to require it. Enterprises are building verification workflows that depend on it.
But watermarking alone doesn't solve the authenticity problem. It's one signal in an emerging verification architecture that will need to integrate multiple provenance methods, work across different content types and model providers, and remain operationally reliable as both generative capabilities and adversarial techniques advance.
Organizations building trust infrastructure around AI-generated content should understand watermarking as a critical capability—but not the only one. The question isn't whether to use watermarks. It's how to integrate watermark detection into a broader verification system that works in a world where not all content is watermarked, not all watermarks are equally robust, and provenance requirements keep changing.
The authenticity layer for AI-generated content is being built right now. Invisible watermarking is a foundational part of that infrastructure—but only one part. Understanding how it works, where it fits, and what it can't do is essential for anyone building systems where synthetic content and trust intersect.
SYNTHETIC PROOF
BEYOND A SINGLE TRUST SIGNAL
See the Wider Trust Picture
Synthetic Proof helps organizations assess trust signals across AI content, prompts, media, and operational workflows.
View Trust and Audit OptionsSynthetic Proof
Verified — Editorial Layer
This content has passed editorial verification for clarity, accuracy, and trust alignment.
Editor-in-Chief: Kevin Marsh
Verification Status: PASSED
Verification Status: PASSED
Comments
Post a Comment