How continuous C2PA manifest appending protects content integrity through every distribution phase. Most organizations treat provenance like a birth certificate—something you create once, file away, and only retrieve when you need to prove where something came from. But in environments where AI models are retrained, datasets are versioned, media assets are transformed, and content travels through editorial pipelines before reaching production, this static approach breaks down almost immediately. The real challenge isn't documenting an asset's origin. It's maintaining an accurate record as that asset evolves through dozens of transformations, approvals, modifications, and ownership changes across its entire lifecycle. The value of provenance ultimately depends on whether organizations can turn evidence into confident decisions. Synthetic Proof helps examine that broader trust picture across AI content and workflows. This is where continuous provenanc...
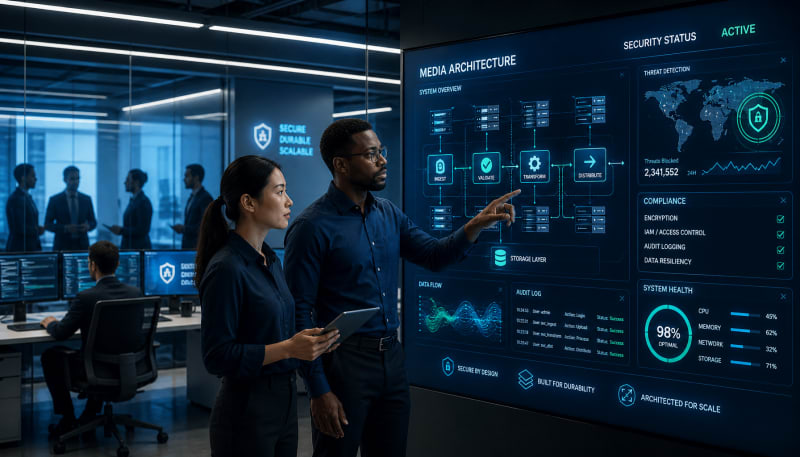
Enterprise blueprint for deploying hybrid verification systems (C2PA + Cloud Lookup + Invisible Watermarks).
Most provenance systems are designed for cooperative environments. They assume participants want to preserve authenticity, that timestamps will remain accessible, and that cryptographic signatures will stay attached to the files they authenticate. This works until someone decides those assumptions no longer serve their interests.
The uncomfortable reality emerging across newsrooms, legal departments, and enterprise content systems is that provenance information is surprisingly fragile. A malicious actor with access to storage systems can strip metadata. A motivated insider can replace cryptographic credentials. A sophisticated adversary can manipulate the infrastructure that verification systems depend on. The question facing organizations building media architectures today isn't whether their provenance will be attacked—it's whether it will survive when it is.
As content history becomes a governance concern, organizations need more than another metadata field. Synthetic Proof provides an independent way to assess provenance, verification, and wider AI trust risk.
Durable provenance represents a fundamental shift in how we think about media authenticity. Rather than asking "how do we prove this content is authentic," the discipline asks "how do we ensure that proof remains intact and verifiable even when someone with significant access and motivation actively tries to destroy it."
The Difference Between Provenance and Durable Provenance
Traditional provenance systems attach authenticity information to media files. They embed metadata describing creation circumstances, apply cryptographic signatures proving the source, and register timestamps establishing when the content came into existence. These mechanisms work well in environments where attackers operate at the edges—strangers attempting to inject fake content or impersonate legitimate sources.
They fail spectacularly when the threat comes from inside the trust boundary.
Durable provenance operates from a different threat model. It assumes adversaries may control file systems, possess valid credentials, have administrative access to content management platforms, and understand exactly how your verification architecture works. Under these conditions, merely attaching authenticity information to a file becomes theatrically insufficient. The provenance infrastructure itself must be designed to resist targeted manipulation.
This distinction matters because the attack surface for media authenticity has fundamentally changed. Organizations once worried primarily about external bad actors creating convincing fakes. Now they must also consider insiders with legitimate access who want to make authentic content disappear, make inauthentic content appear legitimate, or simply create enough ambiguity that nothing can be verified with confidence.
What Makes Provenance Fragile
The vulnerabilities in typical provenance implementations follow predictable patterns. Metadata lives inside file headers that can be rewritten. Cryptographic signatures depend on key infrastructure that can be compromised. Timestamps rely on centralized authorities that can be manipulated or coerced. Verification systems check information stored in databases an attacker may control.
Even blockchain-based approaches—often positioned as inherently durable—prove surprisingly vulnerable to sophisticated tampering. An attacker doesn't need to compromise the blockchain itself if they can simply replace the content the blockchain points to, manipulate the systems performing verification queries, or create ambiguity about which blockchain record corresponds to which physical file.
The deeper problem is architectural. Most provenance systems treat authenticity as a property of individual files rather than a property of the infrastructure managing those files. When your verification logic asks "is this file authentic," it's really asking "does the metadata attached to this file claim it's authentic." An adversary who understands this distinction can attack the question rather than the answer.
Organizations discover these vulnerabilities at the worst possible moments. A legal team prepares to submit video evidence only to find timestamps have been systematically altered. A newsroom realizes published images lack verifiable provenance because metadata was stripped during normal content workflow. A regulatory investigation reveals that audit trails can't distinguish between legitimate updates and malicious manipulation because both used the same administrative credentials.
Architectural Principles for Durability
Building provenance systems that survive determined attacks requires rethinking how authenticity information integrates with media infrastructure. Several architectural principles distinguish durable implementations from fragile ones.
First, provenance must be decoupled from content. Rather than embedding authenticity information inside files where it can be modified or stripped, durable architectures maintain independent verification layers that can't be altered by manipulating the media itself. This doesn't mean abandoning embedded metadata—it means ensuring that metadata serves as convenience rather than source of truth.
Second, verification must remain possible even when specific infrastructure components are compromised. If an attacker gains control of your content management system, can provenance still be verified? If credentials are stolen, does your entire authenticity framework collapse? Durable architectures assume breach and build verification paths that don't depend on single points of failure.
Third, the system must create evidence of tampering rather than simply failing silently when manipulation occurs. Organizations need to know not just that provenance is missing, but that it was removed. Not just that verification failed, but why it failed and what changed. This forensic capability transforms provenance from a binary check into an investigative tool.
Fourth, durability requires thinking beyond technical controls to include procedural and organizational measures. Separation of duties ensures that people who can modify content can't also modify provenance records. Independent attestation creates external verification that can't be compromised through internal access. Regular audits verify that durability mechanisms remain intact and effective.
The Insider Threat Drives Architecture
The most significant shift in provenance thinking involves accepting that many attacks will come from people who already have legitimate access to your systems. This isn't about paranoia—it's about realistic threat modeling.
Insiders possess advantages external attackers can't match. They understand your verification architecture. They know which systems are monitored and which aren't. They have credentials that grant broad access. They can modify content gradually over time rather than triggering the anomaly detection that bulk tampering would create. Most importantly, they can attack the verification infrastructure itself rather than just the content it protects.
Durable provenance architectures respond by assuming compromise. They create verification chains that require collusion across multiple individuals and systems. They maintain independent records that can detect when primary systems have been manipulated. They generate audit trails that themselves have provenance, making it difficult to cover tracks without creating additional evidence.
This doesn't mean treating every employee as a threat. It means recognizing that credential theft, coercion, and honest mistakes create insider-equivalent scenarios even in organizations with impeccable security culture. The architecture needs to maintain integrity regardless of who gained access or why.
Verification Must Work Decades Later
Durability has a temporal dimension that many organizations overlook. Provenance isn't just about proving authenticity today—it's about maintaining that proof years or decades into the future when the original creation context has disappeared.
This creates unexpected challenges. Cryptographic algorithms become obsolete. Organizations managing key infrastructure cease to exist. File formats evolve beyond backward compatibility. The people who created the content move to other companies or retire. The systems that generated timestamps get decommissioned. The context everyone "just knew" when the content was created becomes opaque to future investigators.
Durable architectures account for this temporal decay. They use cryptographic approaches that anticipate algorithm obsolescence. They create provenance records comprehensible without access to proprietary systems. They maintain enough context that future verification doesn't depend on institutional memory. They plan for the organization itself potentially not existing when verification becomes necessary.
Legal and regulatory contexts amplify this temporal requirement. Evidence submitted in litigation may need verification years after creation. Regulatory audits can examine content from previous compliance periods. Historical archives require authenticity guarantees that outlast the technology stack that created them. Provenance that works today but fails in five years isn't actually durable—it's deferred failure.
The Cost of Fragility Is Increasing
Organizations could once treat provenance as a nice-to-have feature. If authenticity information was missing or questionable, the reputational and operational impact remained manageable. That calculus is changing rapidly.
Regulatory frameworks increasingly require not just that content be authentic, but that authenticity be demonstrable. Courts are beginning to exclude evidence lacking robust provenance. Media organizations face credibility crises when they can't verify their own published content. Enterprise customers demand authenticity guarantees in service agreements. Insurance policies now include provisions around content verification capabilities.
The deepfake phenomenon accelerates this shift. As synthetic media becomes more convincing, the burden of proof reverses. Organizations must affirmatively demonstrate authenticity rather than forcing skeptics to prove manipulation. This makes provenance infrastructure a precondition for content having evidentiary value rather than a supplementary feature.
Perhaps more significantly, adversaries are becoming sophisticated about attacking provenance rather than just creating fake content. The most damaging manipulation isn't creating a convincing fake—it's making authentic content unverifiable, creating confusion about what's real, or generating enough provenance ambiguity that truth becomes indistinguishable from fabrication. Against these attacks, fragile provenance systems become liabilities rather than assets.
Final Thoughts
The transition from provenance to durable provenance reflects organizational maturity in thinking about media authenticity. Early implementations focused on the technical challenge of cryptographically signing content. Intermediate approaches recognized the need for comprehensive metadata and third-party verification. Durable architectures accept that provenance infrastructure itself becomes a target and must survive determined attacks by adversaries with significant capabilities and access.
This evolution matters because the value of content increasingly depends on verifiable authenticity. Media without durable provenance isn't just less trustworthy—it's becoming less usable. Organizations building content infrastructure today must ask whether their authenticity mechanisms will survive not just benign neglect but active, sophisticated attempts to undermine them.
The Practical Position
Provenance that can be deleted by someone with administrative credentials isn't provenance—it's documentation. The organizations building resilient content systems now recognize that authenticity mechanisms must be architected to outlast the access privileges of any individual actor, including insiders who understand exactly how verification works and possess legitimate system authority.
— Kevin Marsh, Editor-in-Chief
SYNTHETIC PROOF
FROM PROVENANCE TO OPERATIONAL TRUST
Understand Your AI Trust Gap
Synthetic Proof helps teams evaluate verification, provenance, prompt risk, and digital media trust through independent audits and structured findings.
Explore Synthetic ProofSynthetic Proof
Verified — Editorial Layer
This content has passed editorial verification for clarity, accuracy, and trust alignment.
Editor-in-Chief: Kevin Marsh
Verification Status: PASSED
Verification Status: PASSED
Comments
Post a Comment