Critical review showing why statistical models produce false positives and why deterministic provenance is superior. For the past several years, the prevailing strategy for combating synthetic media has been detection: build better classifiers, train on larger datasets, identify artifacts faster than generative models can eliminate them. The logic seemed sound. If AI can create deepfakes, AI can also detect them. Except it hasn't worked. The value of provenance ultimately depends on whether organizations can turn evidence into confident decisions. Synthetic Proof helps examine that broader trust picture across AI content and workflows. Detection-based approaches have reached an operational ceiling. They struggle against modern generative models, degrade rapidly as those models improve, and offer no mechanism to verify authenticity when detection fails. Organizations deploying deepfake detectors today are discovering what researchers have known quietly for s...
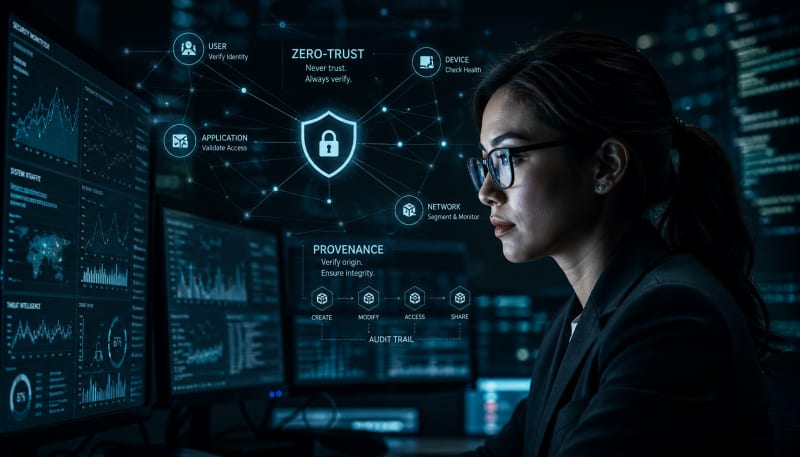
Why modern threat vectors require security teams to verify media identity rather than analyze pixels.
For decades, cybersecurity has operated on a simple premise: build walls high enough to keep threats out, and when they inevitably get through, detect them quickly enough to minimize damage. Organizations have spent billions on firewalls, intrusion detection systems, endpoint protection, and increasingly sophisticated monitoring tools. Yet despite these investments, breaches continue to accelerate, supply chain attacks proliferate, and the window between infiltration and detection continues to measure in months rather than minutes.
The problem isn't that detection has failed. It's that detection alone was never enough.
The value of provenance ultimately depends on whether organizations can turn evidence into confident decisions. Synthetic Proof helps examine that broader trust picture across AI content and workflows.
A different approach is emerging across enterprise security teams, particularly among organizations navigating AI adoption, synthetic content, and increasingly complex digital supply chains. Rather than asking "Can we detect this threat faster?" they're asking a fundamentally different question: "Can we verify the origin and integrity of everything flowing through our systems before we trust it?"
This shift represents more than incremental improvement. It marks the beginning of what's becoming known as zero-trust provenance—a paradigm where trust is never assumed and every asset, model, prompt, output, and data artifact carries verifiable evidence of its origin and transformation history.
The Detection Model Wasn't Built for Today's Threat Landscape
Traditional cybersecurity operates reactively. A threat enters the environment, triggers an alert, and security teams respond. The sophistication lies in how quickly systems can identify anomalies and how effectively teams can contain damage.
This worked reasonably well when threats were external actors attempting to breach network perimeters. It becomes considerably less effective when threats originate from compromised credentials, poisoned training data, manipulated AI models, or synthetic content that appears entirely legitimate until it's already been acted upon.
Consider the security implications of AI adoption. Organizations are deploying models trained on third-party datasets, using prompt templates from multiple sources, integrating outputs into decision systems, and automating workflows based on AI-generated recommendations. Each point in this chain represents a potential compromise vector—not through traditional malware, but through subtle manipulation that detection systems were never designed to catch.
A poisoned training dataset doesn't trigger intrusion alerts. A manipulated model doesn't behave like ransomware. A compromised prompt doesn't resemble a network scan. Yet each can fundamentally undermine trust in systems making consequential decisions.
Detection assumes you know what threats look like. Provenance assumes you verify what trust requires.
What Zero-Trust Provenance Actually Means
Zero-trust as a security framework is well established: never trust, always verify. Zero-trust provenance extends this principle beyond network access to the artifacts themselves—the models, datasets, prompts, outputs, and content flowing through enterprise systems.
Rather than verifying identity at the perimeter and trusting everything inside, zero-trust provenance requires continuous verification of digital artifacts throughout their lifecycle. Where did this model originate? What data was it trained on? Has it been modified since deployment? What prompts generated this output? Can we cryptographically verify this chain of custody?
This isn't about detecting anomalies after the fact. It's about establishing verifiable integrity before trust is granted.
The technical foundation involves several converging capabilities. Cryptographic attestation provides tamper-evident records of artifact creation and transformation. Immutable logging captures provenance chains that can't be retroactively altered. Digital signatures bind artifacts to verified sources. Content credentials embed machine-readable provenance directly into digital assets.
Together, these technologies enable organizations to answer questions that detection-based security simply cannot address: Is this the model we intended to deploy, or has it been altered? Did this output actually come from our approved system, or is it synthetic content masquerading as legitimate? Can we prove the lineage of this decision to auditors, regulators, or customers?
The Operational Challenge Detection Never Solved
Detection tells you something went wrong. Provenance tells you whether to trust something in the first place.
This distinction becomes critical as organizations face regulatory requirements around AI transparency, model governance, and algorithmic accountability. Detecting that a model behaved unexpectedly doesn't help you demonstrate to regulators what data it was trained on, how it was validated, or whether it meets compliance requirements.
Provenance infrastructure creates verifiable audit trails that exist independent of the systems being audited. This matters enormously for governance, but it also fundamentally changes security posture. When every artifact carries cryptographic evidence of its origin and transformation history, compromised components become detectable not through behavioral analysis but through broken provenance chains.
Provenance Is Moving From Project to Infrastructure
Early implementations of provenance verification emerged as point solutions—individual teams tracking model lineage for specific compliance requirements, creative organizations embedding metadata in synthetic media, or research groups documenting dataset origins for reproducibility.
What's changing is the recognition that provenance cannot remain a specialized practice confined to particular use cases. As AI systems become infrastructure rather than experiments, provenance must become infrastructure as well.
This shift is visible across multiple domains. Content authentication standards are moving from voluntary adoption to platform integration. Model registries are evolving from tracking systems to verification infrastructure. Prompt management is expanding from workflow optimization to security controls. Supply chain verification is extending beyond software packages to encompass training data, model weights, and AI-generated components.
The operational model emerging in forward-looking organizations treats provenance as a foundational layer rather than an add-on capability. Just as identity and access management became standard infrastructure rather than optional tooling, provenance verification is becoming an expected component of responsible AI deployment.
This doesn't mean every organization is building comprehensive provenance systems today. It means the market is recognizing that trust infrastructure—the systems that verify, attest, and document AI artifact integrity—represents a category requirement rather than a nice-to-have feature.
Why Security Teams Are Paying Attention Now
Several converging pressures are accelerating this transition beyond theoretical frameworks into operational reality.
Regulatory requirements are becoming explicit about provenance and transparency. The EU AI Act requires documentation of training data and model development processes. Industry-specific regulations increasingly demand audit trails that detection-based security cannot provide. Organizations implementing AI governance frameworks discover quickly that governance requires verifiable provenance.
Supply chain attacks have demonstrated that trusting components based on source reputation is insufficient. The compromise doesn't need to happen inside your perimeter—it can occur upstream in training pipelines, model repositories, or data processing workflows. By the time malicious components reach your environment, they appear entirely legitimate to detection systems.
Perhaps most significantly, organizations are discovering that AI introduces trust dependencies that traditional security tools weren't designed to address. When business processes rely on AI outputs, the integrity of those outputs becomes a foundational security concern. Detection can identify when systems behave abnormally. It cannot verify whether the AI making recommendations has been subtly compromised to favor particular outcomes.
Zero-trust provenance provides the verification layer these scenarios require.
The Integration Challenge Nobody Is Ignoring
Understanding why zero-trust provenance matters is considerably easier than implementing it across existing security architectures, development pipelines, and operational workflows.
The technical challenges are real. Cryptographic attestation requires key management at scale. Immutable logging generates substantial data volumes. Provenance verification adds latency to workflows optimized for speed. Integration with existing security information and event management systems, identity platforms, and compliance frameworks requires coordination across multiple teams.
The operational challenges may be harder. Security teams must shift from reactive detection mindsets to proactive verification models. Developers must incorporate provenance documentation into build processes. Data scientists must track training data lineage. Compliance teams must define what provenance evidence actually proves.
This is why provenance infrastructure is emerging as a distinct category rather than remaining a collection of internal tools. The complexity of building comprehensive, cryptographically verifiable, independently auditable provenance systems across diverse AI workflows exceeds what most organizations can reasonably construct internally.
Organizations serious about zero-trust provenance are increasingly looking toward specialized trust infrastructure—independent verification layers that sit between AI systems and the business processes that depend on them, providing attestation, audit trails, and verification capabilities without requiring complete workflow redesign.
What This Means for Security Architecture
Zero-trust provenance doesn't replace detection. It establishes the foundation detection requires to function effectively in AI-driven environments.
Detection systems identify anomalies. Provenance systems verify integrity. Together, they create security architectures capable of addressing both traditional threats and the novel risks introduced by AI adoption, synthetic content, and automated decision systems.
The practical implication is that security architectures increasingly require trust infrastructure as a distinct layer. Identity and access management verifies who should access systems. Provenance infrastructure verifies what should be trusted within those systems. Detection identifies when trust assumptions are violated.
This layered approach is becoming visible in enterprise security roadmaps. Organizations aren't abandoning existing detection capabilities—they're augmenting them with verification infrastructure that provides the provenance guarantees governance requires and security teams need.
Final Thoughts
The shift from threat detection to zero-trust provenance represents a maturation of enterprise security thinking. Detection remains essential, but it's no longer sufficient when the artifacts flowing through systems—models, prompts, outputs, synthetic content—can be subtly compromised in ways traditional security tools cannot identify.
Zero-trust provenance establishes a fundamentally different security posture: rather than detecting threats after they've entered trusted environments, it requires continuous verification of artifact integrity before trust is granted. This approach aligns naturally with AI governance requirements, regulatory expectations, and the operational realities of deploying AI at scale.
The organizations implementing provenance infrastructure today aren't doing so because the technology is mature or the integration is simple. They're doing so because the alternative—continuing to operate AI systems without verifiable provenance—creates risks that detection alone cannot mitigate and governance frameworks cannot accept.
As AI moves from experimental projects to operational infrastructure, the trust infrastructure supporting it must make the same transition. Zero-trust provenance isn't replacing cybersecurity's existing paradigm. It's building the verification layer that paradigm always assumed existed but never actually implemented.
The Practical Position
The organizations restructuring security architectures around provenance rather than perimeter defense aren't reacting to the latest threat—they're acknowledging that trust itself has become the attack surface. When artifacts carry no verifiable history, detection becomes forensics performed too late. Zero-trust provenance doesn't supplement existing security models; it replaces the assumption that legitimate-looking assets are safe to execute.
— Kevin Marsh, Editor-in-Chief
SYNTHETIC PROOF
FROM PROVENANCE TO OPERATIONAL TRUST
Understand Your AI Trust Gap
Synthetic Proof helps teams evaluate verification, provenance, prompt risk, and digital media trust through independent audits and structured findings.
Explore Synthetic ProofSynthetic Proof
Verified — Editorial Layer
This content has passed editorial verification for clarity, accuracy, and trust alignment.
Editor-in-Chief: Kevin Marsh
Verification Status: PASSED
Verification Status: PASSED
Comments
Post a Comment