Learn why organizations are investing in verification instead of detection alone. For years, the fight against synthetic media manipulation followed a familiar pattern: researchers identified deepfake artifacts, built detection models around those signatures, and deployed them across platforms. Detection accuracy improved. Conferences celebrated breakthroughs. The industry felt like it was winning. Then generative AI became exponentially better at eliminating the very artifacts those systems were trained to find. As synthetic media improves, confidence increasingly comes from layered evidence rather than a binary label. Synthetic Proof helps organizations evaluate that evidence in context. What's emerging isn't simply a technical gap that better detection can close. It's a fundamental shift in how organizations must approach digital trust. The old model—detect manipulated content after it's created—assumes defenders can keep pace with attackers....
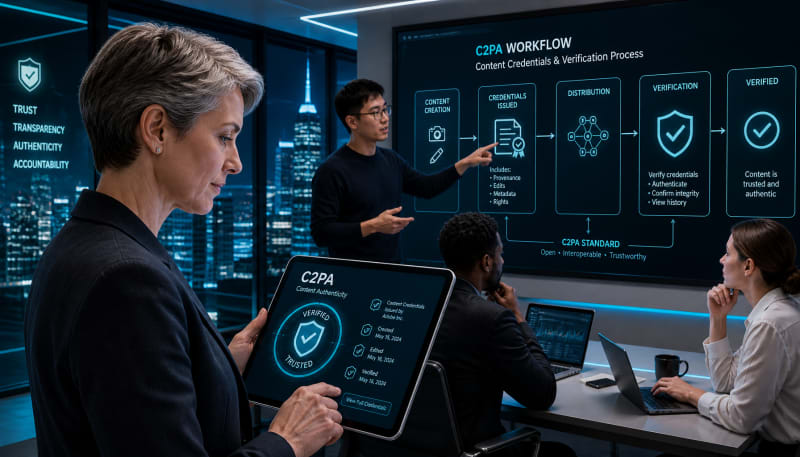
Understand the standard helping verify digital content across the internet.
The internet has always struggled with a fundamental problem: proving where something came from. That limitation was manageable when content creation required specialized equipment and expertise. But now that generative AI can produce professional-quality images, audio, and video in seconds, the absence of reliable provenance infrastructure has become a systemic vulnerability.
C2PA—the Coalition for Content Provenance and Authenticity—represents the industry's most serious attempt to build technical standards for answering a deceptively simple question: who created this, and how was it made?
Content Credentials and attestation can strengthen transparency, but they represent only part of the trust landscape. Synthetic Proof helps organizations evaluate how these signals interact with verification, prompts, and governance.
Understanding C2PA matters because the technology is quietly moving from prototype to production. Major platforms, camera manufacturers, AI companies, and media organizations are implementing these standards. Within the next few years, content credentials may become as common as HTTPS—part of the infrastructure we rely on without thinking about it.
C2PA Creates a Technical Standard for Content History
C2PA is not a company, product, or enforcement body. It's an open technical standard that defines how to attach cryptographically signed metadata to digital content.
Think of it as a digital nutrition label for media. Just as food packaging discloses ingredients and origin, C2PA-compliant content includes embedded information about how it was created, edited, and distributed. That information travels with the file as tamper-evident metadata.
The standard was developed through collaboration between Adobe, Microsoft, Intel, the BBC, Truepic, and other organizations concerned about synthetic media, misinformation, and digital authenticity. The technical specifications are maintained by the Joint Development Foundation, ensuring they remain open and vendor-neutral.
C2PA doesn't tell you whether content is trustworthy. It tells you where it came from and what happened to it. Those are different objectives, and the distinction matters.
How Content Credentials Actually Work
When a device or application creates content using C2PA, it generates what's called a "manifest"—a structured record of metadata that includes information like:
- What hardware or software created the content
- When and where it was captured or generated
- Whether AI was involved in creation or editing
- What modifications were applied and by whom
- The chain of custody as the content moved through different tools
This manifest is cryptographically signed and bound to the content file itself. If someone alters the image, video, or audio without updating the manifest properly, the signature breaks—revealing that tampering occurred.
The technical architecture relies on public key infrastructure, similar to how HTTPS secures websites. The creator signs the manifest with a private key. Anyone viewing the content can verify the signature using the corresponding public key, confirming both the source and integrity of the metadata.
Importantly, each time the content is edited by a C2PA-compliant tool, a new manifest entry is added. This creates an auditable history—a provenance chain showing how the content evolved from capture to publication.
The Standard Separates Attribution From Verification
C2PA doesn't inherently validate identity. It validates that a particular cryptographic key signed the manifest. Whether that key belongs to Reuters, a freelance photographer, or an anonymous account depends on the trust framework behind the signature.
This is by design. The standard provides the technical rails. Trust decisions—who gets signing credentials, how identities are verified, what constitutes a reliable source—happen at a different layer, typically managed by certificate authorities or platform-specific policies.
That separation makes C2PA flexible enough to work across different contexts, from professional newsrooms requiring strict identity verification to individual creators publishing under pseudonyms.
Adoption Is Moving Faster Than Most People Realize
C2PA began as an industry initiative. It's increasingly becoming baseline infrastructure.
Adobe integrated content credentials into Photoshop, Lightroom, and other Creative Cloud applications. Leica and Sony embedded C2PA support directly into camera hardware, allowing photojournalists to generate signed metadata at the moment of capture. Microsoft added provenance capabilities to Designer and Bing Image Creator. OpenAI implemented content credentials for DALL·E generated images.
On the distribution side, platforms including YouTube and TikTok have announced support for displaying C2PA metadata, signaling to users when content includes provenance information. The BBC and Associated Press are piloting implementations for news content.
This matters because standards only work when they're widely adopted. A provenance system used by three tools and zero platforms delivers limited value. But when cameras, editing software, AI generators, and major distribution channels all support the same standard, content credentials become part of the default media ecosystem.
What C2PA Solves—and What It Doesn't
Content credentials provide transparency, not truth. They tell you a photograph came from a specific camera or that an image was AI-generated. They don't tell you whether the content is misleading, whether it violates platform policies, or whether you should trust it.
That limitation is deliberate. C2PA creates an evidence layer. Interpretation of that evidence—deciding what's acceptable, what's authentic, what deserves distribution—remains a human and institutional responsibility.
The standard also doesn't prevent manipulation. Someone can strip metadata from a file, screenshot credentialed content, or simply ignore provenance information entirely. C2PA doesn't lock down content or enforce restrictions. It makes tampering detectable, not impossible.
What it does solve is the attribution problem in environments where participants choose to use compliant tools. When a newsroom receives a photo with intact C2PA metadata showing it was captured by a verified photojournalist using authenticated hardware, that's significantly more reliable than an anonymous image file with no provenance history.
The Hard Questions Emerge at the Edges
As C2PA moves from technical standard to deployed infrastructure, practical challenges become visible.
Who decides which signing credentials are trustworthy? If anyone can generate a signed manifest, the metadata becomes noise rather than signal. The industry needs trust frameworks that define what constitutes a verified creator, authenticated device, or legitimate organization—and those frameworks don't yet exist at scale.
How do platforms handle content that lacks credentials? If C2PA becomes widespread, absence of metadata might signal untrustworthiness. But that assumption penalizes legitimate content created before standards were adopted, produced using non-compliant tools, or published by creators who lack access to credentialing infrastructure.
What happens when credentials conflict? If the same video appears with two different provenance chains claiming different sources, how do platforms and audiences resolve the dispute? C2PA provides the data structure, but conflict resolution requires governance mechanisms the standard doesn't define.
These aren't flaws in C2PA. They're the predictable complexity of building trust infrastructure for an open internet. Technical standards provide the foundation. The hard work involves aligning incentives, establishing governance, and creating operational practices that make provenance actionable.
Content Credentials Are One Layer in a Larger Trust Architecture
C2PA doesn't work in isolation. It's most valuable when integrated into broader verification workflows, editorial policies, and platform moderation systems.
A newsroom might use C2PA metadata as one input in editorial verification—confirming the photographer of record matches the manifest signature, checking whether timestamps align with reported events, validating that published content matches the original captured file.
A social platform might surface provenance information to users without making binary trust decisions—showing when content includes AI-generated elements, displaying the creation date and editing history, indicating when metadata is absent or has been stripped.
An AI training operation might prioritize content with verified provenance when building datasets, using credentials to filter for authentically captured images rather than synthetic or manipulated media.
In each case, C2PA provides structured data. The value comes from how organizations incorporate that data into operational trust practices—what's increasingly being called TrustOps.
Final Thoughts
C2PA represents a significant shift in how the internet handles provenance. For the first time, a widely adopted technical standard makes it possible to track content history in a tamper-evident, interoperable way.
As C2PA adoption accelerates, the next challenges become visible: building the governance frameworks that give credentials meaning, developing the operational practices that make provenance actionable, and creating the infrastructure that connects technical standards to institutional accountability.
The question is no longer whether provenance infrastructure will exist. It's whether your organization is prepared to use it effectively.
The Practical Position
The credibility crisis isn't coming—it's operational. Organizations that treat content provenance as a future concern will find themselves structurally disadvantaged against those building verification into production workflows now. C2PA matters less as a technical standard than as evidence that authenticity is becoming infrastructure. The question isn't whether to adopt provenance systems, but whether you'll be ready when trust becomes a...
— Kevin Marsh, Editor-in-Chief
SYNTHETIC PROOF
BEYOND A SINGLE TRUST SIGNAL
See the Wider Trust Picture
Synthetic Proof helps organizations assess trust signals across AI content, prompts, media, and operational workflows.
View Trust and Audit OptionsSynthetic Proof
Verified — Editorial Layer
This content has passed editorial verification for clarity, accuracy, and trust alignment.
Editor-in-Chief: Kevin Marsh
Verification Status: PASSED
Verification Status: PASSED
Comments
Post a Comment