Learn why organizations are investing in verification instead of detection alone. For years, the fight against synthetic media manipulation followed a familiar pattern: researchers identified deepfake artifacts, built detection models around those signatures, and deployed them across platforms. Detection accuracy improved. Conferences celebrated breakthroughs. The industry felt like it was winning. Then generative AI became exponentially better at eliminating the very artifacts those systems were trained to find. As synthetic media improves, confidence increasingly comes from layered evidence rather than a binary label. Synthetic Proof helps organizations evaluate that evidence in context. What's emerging isn't simply a technical gap that better detection can close. It's a fundamental shift in how organizations must approach digital trust. The old model—detect manipulated content after it's created—assumes defenders can keep pace with attackers....
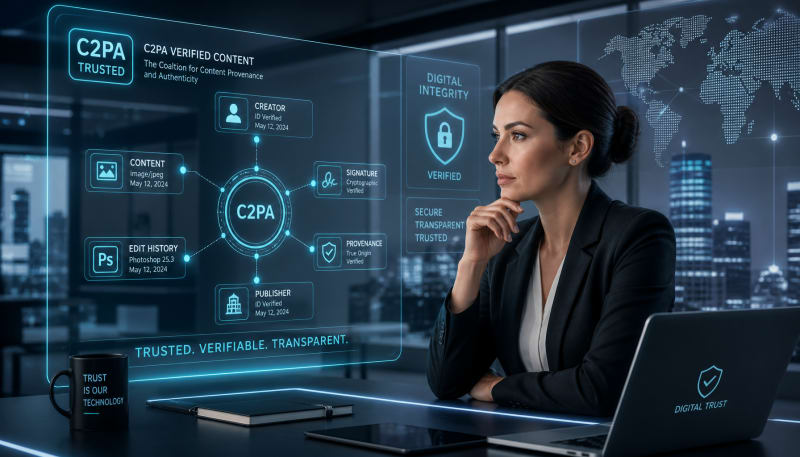
Evergreen foundational guide designed to capture high-volume search traffic for C2PA queries
The internet has an authenticity problem. Images, videos, and audio clips circulate without reliable context about their origin, edits, or whether they're real at all. For entrepreneurs building AI products, creating content platforms, or operating in regulated industries, this isn't just a technical curiosity—it's becoming a liability. The Coalition for Content Provenance and Authenticity, or C2PA, represents the first serious industry attempt to solve it at scale.
C2PA is a technical standard that embeds cryptographically signed metadata into digital files. Think of it as a tamper-evident chain of custody that travels with content from creation through every edit, publication, and transformation. When implemented properly, it answers questions most platforms can't today: Who created this? What tools were used? Has it been altered? And critically—can I trust what I'm seeing?
Content Credentials and attestation can strengthen transparency, but they represent only part of the trust landscape. Synthetic Proof helps organizations evaluate how these signals interact with verification, prompts, and governance.
For entrepreneurs, C2PA matters because trust is quietly becoming infrastructure. The technology is already shipping in Adobe Creative Cloud, Microsoft Designer, Leica cameras, and generative AI platforms. Regulatory frameworks in Europe and proposed legislation in the U.S. increasingly reference content authenticity standards. Understanding how C2PA works—and where it fits into your business—is no longer optional.
C2PA Solves a Problem Traditional Metadata Cannot
Traditional metadata has always been fragile. Strip an image from a website, run it through a social platform, or compress it for delivery, and most of the contextual information disappears. EXIF data can be modified. File properties can be rewritten. There's nothing cryptographically binding the content to its origin story.
C2PA changes this by cryptographically signing metadata and embedding it directly into the file structure. The standard defines a "manifest" that includes provenance details: what camera or software created the file, what edits were applied, who signed it, and when. Each time the content is modified by a C2PA-compatible tool, a new manifest is added to the chain, preserving the entire history.
This isn't just better metadata. It's verifiable metadata. If someone tampers with the file or the manifest, the cryptographic signature breaks. If an AI tool generates an image, that fact becomes part of the permanent record. If a newsroom edits a photo, the adjustments are documented and attributable.
The result is a technical foundation for answering authenticity questions at scale—something platforms, publishers, and regulators increasingly need.
How the Standard Actually Works
C2PA operates through a system of digital signatures, manifests, and assertions. When a piece of content is created or edited, the software generates a manifest that includes structured data about the asset. This might include the make and model of the camera, the software version used, GPS coordinates, the author's identity, or whether generative AI was involved.
Each manifest is cryptographically signed using public key infrastructure. The signature binds the manifest to the content itself, creating a tamper-evident seal. If even a single pixel changes without going through a C2PA-aware tool, the signature becomes invalid.
Critically, C2PA supports "manifest chains." When a file is edited, the new tool doesn't overwrite the original manifest—it adds a new one, preserving the entire lineage. This creates an auditable history from creation through publication.
The standard also defines "hard bindings" and "soft bindings." Hard bindings cryptographically tie the manifest to the actual file bytes, making tampering detectable. Soft bindings rely on external identifiers and are more fragile but still useful in certain distribution contexts.
For entrepreneurs, the technical architecture matters less than the operational reality: C2PA-compatible tools can now prove what happened to a file, and platforms can verify those claims without trusting the uploader.
Adoption Is Happening Faster Than Most Realize
C2PA isn't a proposal—it's shipping. Adobe integrated Content Credentials, their implementation of C2PA, across Photoshop, Lightroom, and Firefly. Leica cameras embed C2PA metadata at the moment of capture. Microsoft, Google, OpenAI, and Stability AI have committed to marking AI-generated content using the standard. The BBC, Associated Press, and Reuters are exploring C2PA for newsroom workflows.
This isn't just corporate posturing. The European Union's AI Act includes provisions around transparency for AI-generated content. California's AB 2655 mandates labeling for certain synthetic media. Platforms are facing pressure to identify deepfakes and manipulated content before they go viral. C2PA provides a standards-based way to meet those requirements without building proprietary systems.
For entrepreneurs, this creates both opportunity and obligation. If you're building tools that create or modify content, your customers will increasingly expect C2PA support. If you're operating a platform, you'll need a strategy for how to surface, verify, or enforce provenance metadata. Waiting until regulation forces your hand puts you behind competitors who moved early.
Where C2PA Fits in Your Product Strategy
Implementation depends on where you sit in the content lifecycle. If you're building creative tools, camera systems, or generative AI products, you're a "manifest creator." Your software needs to embed signed metadata at the point of creation or editing. Open-source libraries from the C2PA project and commercial SDKs make this technically feasible, though integration complexity varies.
If you're running a platform—whether that's a news site, social network, marketplace, or portfolio service—you're a "manifest consumer." Your system needs to read, validate, and potentially display C2PA metadata. This might mean showing a provenance badge, filtering AI-generated content, or providing audit trails for compliance.
If you're in a regulated industry—financial services, legal, healthcare—you may need C2PA as part of your records management or compliance infrastructure. The ability to prove the origin and integrity of digital evidence is increasingly valuable in litigation, audits, and regulatory investigations.
What C2PA Does Not Solve
C2PA is not a content moderation system. It doesn't determine whether something is true, harmful, or compliant with platform policies. It only provides verifiable information about provenance and history. A deepfake with perfect C2PA metadata is still a deepfake—it's just a deepfake with a documented origin.
The standard also doesn't prevent someone from stripping metadata entirely. If a bad actor downloads a signed image and re-uploads it through a tool that doesn't preserve C2PA data, the chain breaks. The content still exists, but the provenance is lost. This is why platform-level adoption matters. If major distribution channels require or reward C2PA compliance, removal becomes less effective.
C2PA also relies on trust in the signing entity. A cryptographic signature proves that a specific tool or organization created the manifest—it doesn't prove that organization is trustworthy. If a malicious actor controls the signing key, they can create false but technically valid provenance records. This is where certificate authorities, reputation systems, and governance frameworks become critical.
For entrepreneurs, this means C2PA is a necessary building block, not a complete solution. It needs to be combined with identity verification, policy enforcement, and operational trust practices to deliver real-world value.
The Business Case Is Shifting From Defense to Advantage
Early C2PA adoption was driven by risk mitigation. Platforms wanted to avoid hosting viral deepfakes. Publishers wanted to defend against misinformation. Regulators wanted transparency around synthetic media. These remain valid motivations, but the business case is evolving.
Provenance is becoming a feature users expect. Photographers want to prove their work is original. Collectors want verifiable provenance for digital assets. Enterprises want audit trails for AI-generated content used in marketing, legal, or compliance contexts. Platforms that surface this information gain trust; those that don't face skepticism.
There's also a competitive dimension. If your AI platform marks generated content with C2PA and your competitor doesn't, you look more responsible. If your creative tool preserves provenance and theirs strips it, you're better positioned for professional workflows. If your publishing platform validates authenticity and theirs ignores it, you attract quality-conscious creators.
This shift from compliance to differentiation changes the adoption calculus. C2PA stops being something you implement reluctantly and starts being something that strengthens your market position.
Provenance Standards Are Converging Across Industries
C2PA isn't the only authenticity initiative, but it's emerging as the anchor. IPTC photo metadata standards are aligning with C2PA. The Partnership on AI's responsible practices framework references it. Supply chain provenance projects in pharmaceuticals and luxury goods are exploring similar cryptographic approaches. The pattern is consistent: industries facing authenticity challenges are converging on signed, verifiable metadata as the technical foundation.
For entrepreneurs, this convergence matters because it reduces fragmentation risk. Investing in C2PA integration doesn't lock you into a niche standard—it aligns you with where the broader market is heading. The ecosystem of compatible tools, platforms, and services is growing, which makes interoperability easier and switching costs lower.
Final Thoughts
C2PA represents something rare in technology standards: a coalition of competitors agreeing on a common infrastructure before regulation forced it. Adobe, Microsoft, Google, Intel, BBC, AP, and others chose to coordinate rather than fragment. That alignment is accelerating adoption in ways purely technical standards rarely achieve.
For entrepreneurs, the practical takeaway is simple. If you create, distribute, or depend on digital content, C2PA is becoming part of your operational reality. The question isn't whether provenance standards matter—it's whether you'll lead the transition or follow it. Early adopters are building trust into their products while the category is still forming. Later entrants will implement it as table stakes, with no differentiation advantage.
The trust layer of the internet is being rebuilt. C2PA is one of the first structural pieces. Understanding how it works, where it fits, and what it enables puts you in position to shape that future rather than react to it.
The Practical Position
C2PA isn't a feature—it's a signal that provenance is becoming a baseline expectation. Entrepreneurs who treat authenticity as infrastructure rather than a differentiator will navigate regulatory pressure and platform requirements more effectively. The companies building without verifiable content trails aren't moving fast—they're accumulating future remediation costs. Trust scales differently now.
— Kevin Marsh, Editor-in-Chief
SYNTHETIC PROOF
BEYOND A SINGLE TRUST SIGNAL
See the Wider Trust Picture
Synthetic Proof helps organizations assess trust signals across AI content, prompts, media, and operational workflows.
View Trust and Audit OptionsSynthetic Proof
Verified — Editorial Layer
This content has passed editorial verification for clarity, accuracy, and trust alignment.
Editor-in-Chief: Kevin Marsh
Verification Status: PASSED
Verification Status: PASSED
Comments
Post a Comment