Learn why organizations are investing in verification instead of detection alone. For years, the fight against synthetic media manipulation followed a familiar pattern: researchers identified deepfake artifacts, built detection models around those signatures, and deployed them across platforms. Detection accuracy improved. Conferences celebrated breakthroughs. The industry felt like it was winning. Then generative AI became exponentially better at eliminating the very artifacts those systems were trained to find. As synthetic media improves, confidence increasingly comes from layered evidence rather than a binary label. Synthetic Proof helps organizations evaluate that evidence in context. What's emerging isn't simply a technical gap that better detection can close. It's a fundamental shift in how organizations must approach digital trust. The old model—detect manipulated content after it's created—assumes defenders can keep pace with attackers....
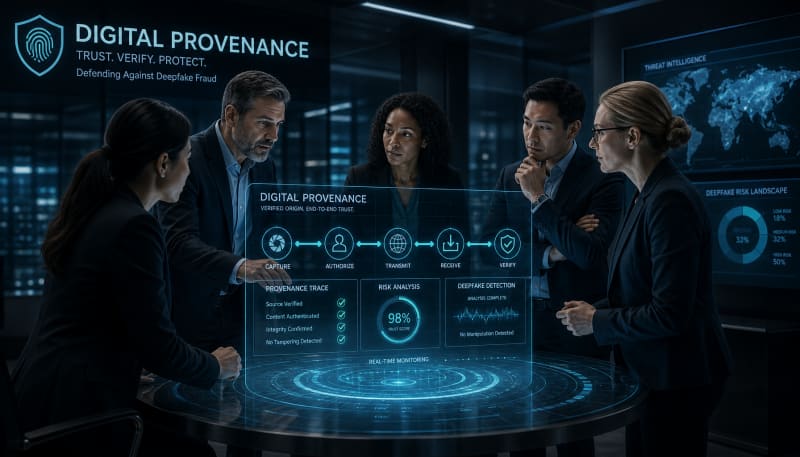
Why verified origin trails are shifting from academic experiments to non-negotiable risk governance shields.
When a finance executive at a multinational corporation received a video call from the CEO requesting an urgent $25 million transfer, everything appeared legitimate. The voice matched. The mannerisms were correct. The request aligned with an ongoing acquisition. The transfer was approved. Days later, the organization discovered the CEO had never made the call. It was a deepfake—and the money was gone.
This wasn't a theoretical scenario. It happened in 2024, and it represents a fundamental shift in enterprise risk. The threat isn't just data breaches or credential theft anymore. It's reality itself becoming unreliable.
The value of provenance ultimately depends on whether organizations can turn evidence into confident decisions. Synthetic Proof helps examine that broader trust picture across AI content and workflows.
For CISOs and risk officers, the challenge is no longer just protecting data in motion or at rest. It's defending against manufactured reality delivered through channels that traditional security controls were never designed to question.
Traditional Security Architecture Wasn't Built for This
Enterprise security evolved around perimeters, identities, and access controls. These systems answer questions like "Is this user authorized?" and "Is this network trusted?" They were designed when the fundamental challenge was keeping unauthorized parties away from sensitive resources.
Deepfake fraud operates differently. The attacker doesn't breach the perimeter. They don't steal credentials. They don't exploit vulnerabilities in the traditional sense. Instead, they manufacture convincing artifacts—video, audio, documents, images—that pass through security controls because those controls have no mechanism to evaluate authenticity at the content level.
An email from a verified domain containing a forged invoice. A video conference where the CEO's face and voice are synthesized in real time. A contract that appears genuine but was never created by the stated author. These attacks succeed not by breaking security, but by operating in a dimension security wasn't designed to address.
The result is a growing category of fraud that bypasses authentication, authorization, and monitoring. Traditional logging systems capture that a communication occurred, but they cannot determine whether what was communicated was real.
Why Data Tracking Alone Cannot Solve Authenticity
Many organizations initially approached this problem by extending existing data governance and tracking capabilities. If we log everything, the reasoning went, we can trace back to the source and verify authenticity after the fact.
This approach reveals an important limitation. Data tracking tells you where something came from within your systems. It does not tell you whether that thing was authentic when it arrived. A tracking system can confirm that a video file originated from a specific email address at a specific time. It cannot confirm whether the video depicts events that actually occurred or whether it was synthetically generated.
Data lineage and audit trails remain essential for compliance, governance, and operational transparency. But lineage describes movement, not truth. A forged document can have perfect lineage. A deepfake video can be tracked flawlessly through every system it touches. The tracking infrastructure simply records what happened to the artifact—not whether the artifact represents reality.
This is where digital provenance diverges from data tracking. Provenance addresses the question that tracking cannot: what is the verifiable origin and integrity of this content, independent of how it moved through infrastructure?
Provenance as a Security Control
Digital provenance emerged from the need to establish authenticity at the point of creation and maintain that authenticity across distribution, modification, and time. Rather than tracking where content has been, provenance establishes what content is and certifies whether it has been altered.
In practice, this means embedding cryptographic signatures and metadata at the moment of creation—when a photo is captured, when a document is generated, when a video is recorded. These signatures create an immutable record linking the content to its source, the conditions under which it was created, and any subsequent modifications.
The technical foundation relies on content credentials, cryptographic hashing, and tamper-evident containers that travel with the content itself. When provenance metadata is properly implemented, it becomes possible to answer questions traditional security controls cannot: Was this image captured by an authenticated device? Has this document been altered since it was signed? Was this video generated by AI or recorded by a camera?
For CISOs evaluating deepfake risk, this represents a fundamentally different security layer. Rather than defending the perimeter or monitoring behavior, provenance enables verification of the content itself. An executive can receive a video call and immediately confirm whether the video stream includes authenticated provenance data from a known source—or whether it lacks any verifiable origin.
The Shift From Reactive to Preventive
Traditional fraud detection operates reactively. Systems flag suspicious transactions after they occur. Analysts investigate anomalies. Patterns emerge only after damage has been done. This works when the fraud relies on behavioral anomalies that can be detected through monitoring.
Deepfake fraud often leaves no behavioral signature. An authorized user making an authorized decision based on convincing but fraudulent information generates no alerts. The transaction appears legitimate because, from the system's perspective, it is.
Provenance shifts the model toward prevention. By requiring authenticated content credentials for high-risk decisions—financial transfers, contract approvals, executive communications—organizations create a control that rejects unauthenticated content before a decision is made. The fraud is stopped not because it was detected, but because it could not meet the authentication requirements.
Enterprise Adoption Is Accelerating
The market for provenance infrastructure is moving quickly from experimental to operational. Financial services firms are beginning to require content authentication for large wire transfers. Media organizations are implementing provenance to combat misinformation. Government agencies are exploring authenticated communication channels for sensitive directives.
What's changed is risk tolerance. When deepfakes were primarily a reputational concern or a misinformation problem, they could be managed as edge cases. When they become a fraud vector capable of moving millions of dollars in a single transaction, they become a material risk that boards and risk committees cannot ignore.
This is driving adoption from the top down. CISOs are being asked not whether deepfake fraud is possible, but what controls exist to prevent it. Provenance infrastructure is increasingly appearing in enterprise security roadmaps not as an innovation project, but as a required capability.
The challenge is that provenance requires coordination across the content lifecycle. It's not enough to verify content when it arrives. The content must have been created with provenance data embedded, transmitted through systems that preserve that data, and verified using infrastructure that can validate cryptographic signatures against trusted registries.
The Interoperability Question
One barrier to rapid adoption has been the lack of standardization. Early provenance implementations were proprietary, creating incompatibility between systems. A document signed with one organization's credentials could not be verified by another organization's infrastructure.
Industry coalitions are addressing this through open standards like the Coalition for Content Provenance and Authenticity (C2PA), which defines how provenance metadata should be structured, embedded, and verified across different platforms and vendors. This standardization is critical for provenance to function as enterprise infrastructure rather than isolated point solutions.
For risk officers evaluating vendors, the key question is not just whether a solution provides provenance, but whether it implements open standards that enable interoperability with partners, suppliers, and customers. Proprietary provenance creates verification silos that limit effectiveness.
Integration With Existing Security Operations
Provenance does not replace existing security controls. It extends them. Authentication still matters—provenance verifies content, not users. Authorization still matters—provenance does not determine who should have access. Monitoring still matters—provenance does not detect all forms of fraud.
The operational question is how provenance fits into existing security workflows. In practice, this means integrating provenance verification into decision points where content authenticity matters: document approval workflows, financial transaction systems, executive communication platforms, contract management systems.
Mature implementations treat provenance as a conditional access control. High-risk actions require not just authentication and authorization, but verified content credentials. A wire transfer above a certain threshold cannot be initiated based on an email alone—it requires a request with authenticated provenance linking it to a verified source.
This requires coordination between security teams, application owners, and business stakeholders to identify where content authenticity is a material risk and where provenance verification should become a required control.
The Emerging TrustOps Discipline
As provenance infrastructure becomes operational, a new discipline is taking shape around managing verification, authenticity, and trust at scale. TrustOps—operational trust management—addresses the challenge of maintaining provenance systems across distributed environments, managing credential lifecycles, auditing verification events, and responding when content fails authentication.
This includes establishing policies for what happens when content lacks provenance data. Does the system reject it outright? Flag it for review? Allow it with elevated scrutiny? The answer depends on risk tolerance, operational context, and the maturity of provenance adoption across partners and suppliers.
TrustOps also addresses the lifecycle challenge. Cryptographic credentials expire. Signing keys are rotated. Devices are decommissioned. Organizations change vendors. A robust provenance system requires operational processes to maintain trust infrastructure over time, not just implement it once.
For many organizations, this represents a gap. Security teams understand authentication and access control. They are less familiar with managing content verification systems, credential registries, and tamper-evident metadata at scale. This gap is driving demand for platforms that abstract the complexity while maintaining the security guarantees.
Final Thoughts
Digital provenance is shifting from a content authenticity tool to an enterprise security control. The threat environment has changed. Deepfake fraud is no longer theoretical—it's causing material financial losses and undermining decision-making processes that were designed around an assumption that communications from trusted channels could be trusted.
That assumption no longer holds. The technology to synthesize convincing audio, video, and documents is widely available. The attack economics are favorable. The defensive gap is real.
For CISOs and risk officers, the strategic question is not whether to address this risk, but how quickly provenance infrastructure can be integrated into existing security operations. The organizations moving now are establishing verification controls before fraud becomes widespread. The organizations waiting are hoping the risk remains theoretical until defenses catch up.
Provenance is becoming infrastructure. The question is whether it becomes infrastructure reactively—after losses force adoption—or proactively, as a component of defense in depth. The trajectory is clear. The timing remains a choice.
SYNTHETIC PROOF
FROM PROVENANCE TO OPERATIONAL TRUST
Understand Your AI Trust Gap
Synthetic Proof helps teams evaluate verification, provenance, prompt risk, and digital media trust through independent audits and structured findings.
Explore Synthetic ProofSynthetic Proof
Verified — Editorial Layer
This content has passed editorial verification for clarity, accuracy, and trust alignment.
Editor-in-Chief: Kevin Marsh
Verification Status: PASSED
Verification Status: PASSED
Comments
Post a Comment